
01 · ISMSIS
Information security
Assess the management system and safeguards used to protect sensitive information across automotive operations and partnerships.
Connect automotive sites, services, assets, suppliers, policies, risks, evidence and remediation around the VDA ISA assessment journey—without reducing readiness to a one-off questionnaire.
The supplied STORM technical description does not list VDA ISA as a current built-in framework. STORM provides documented governance and assessment building blocks; confirm catalogue content and mappings before use.
VDA ISA is the requirements catalogue underlying TISAX. The selected assessment objectives determine which catalogue content, questions and requirement levels apply to the organisation's scope.
Assess the management system and safeguards used to protect sensitive information across automotive operations and partnerships.
Address high or very high confidentiality needs according to the information handled for automotive partners.
Address availability needs where disruption to products or services could quickly affect a customer's ability to produce or deliver.
Cover relevant prototype parts, vehicles, test vehicles, events and associated physical or organisational safeguards.
Address processor responsibilities for personal data and, where relevant, special categories of personal data.
Create a common assessment baseline for manufacturers, suppliers, service providers, engineering partners and software organisations.
The technical description documents configurable assessments and extensive evidence workflows, but it does not name VDA ISA among STORM's current built-in frameworks.
Use documented STORM capabilities to organise the operational record behind an automotive security programme while official ISA content, maturity interpretation and TISAX assessment decisions remain outside the product claim.
Model locations, services, processes, data, hardware, software, users and external providers together with their dependencies.
Sites · assets · servicesCreate tailored internal or supplier questionnaires, track implementation status, compare periods and schedule reassessments.
Self-assessment · reviewLet suppliers complete assigned questionnaires, upload supporting evidence per control and make submissions available for review.
Portal · evidence · oversightCapture risks, likelihood, impact, controls, treatment decisions, mitigation plans, owners, dates and supporting attachments.
Risk register · actionsManage policy authoring, versions, approvals, acknowledgements, scheduled reviews and mappings with a retained audit trail.
Policy Center · lifecycleConsolidate findings, risks, incidents, supplier results, policy status and improvement actions into structured oversight records.
Audit · review · reporting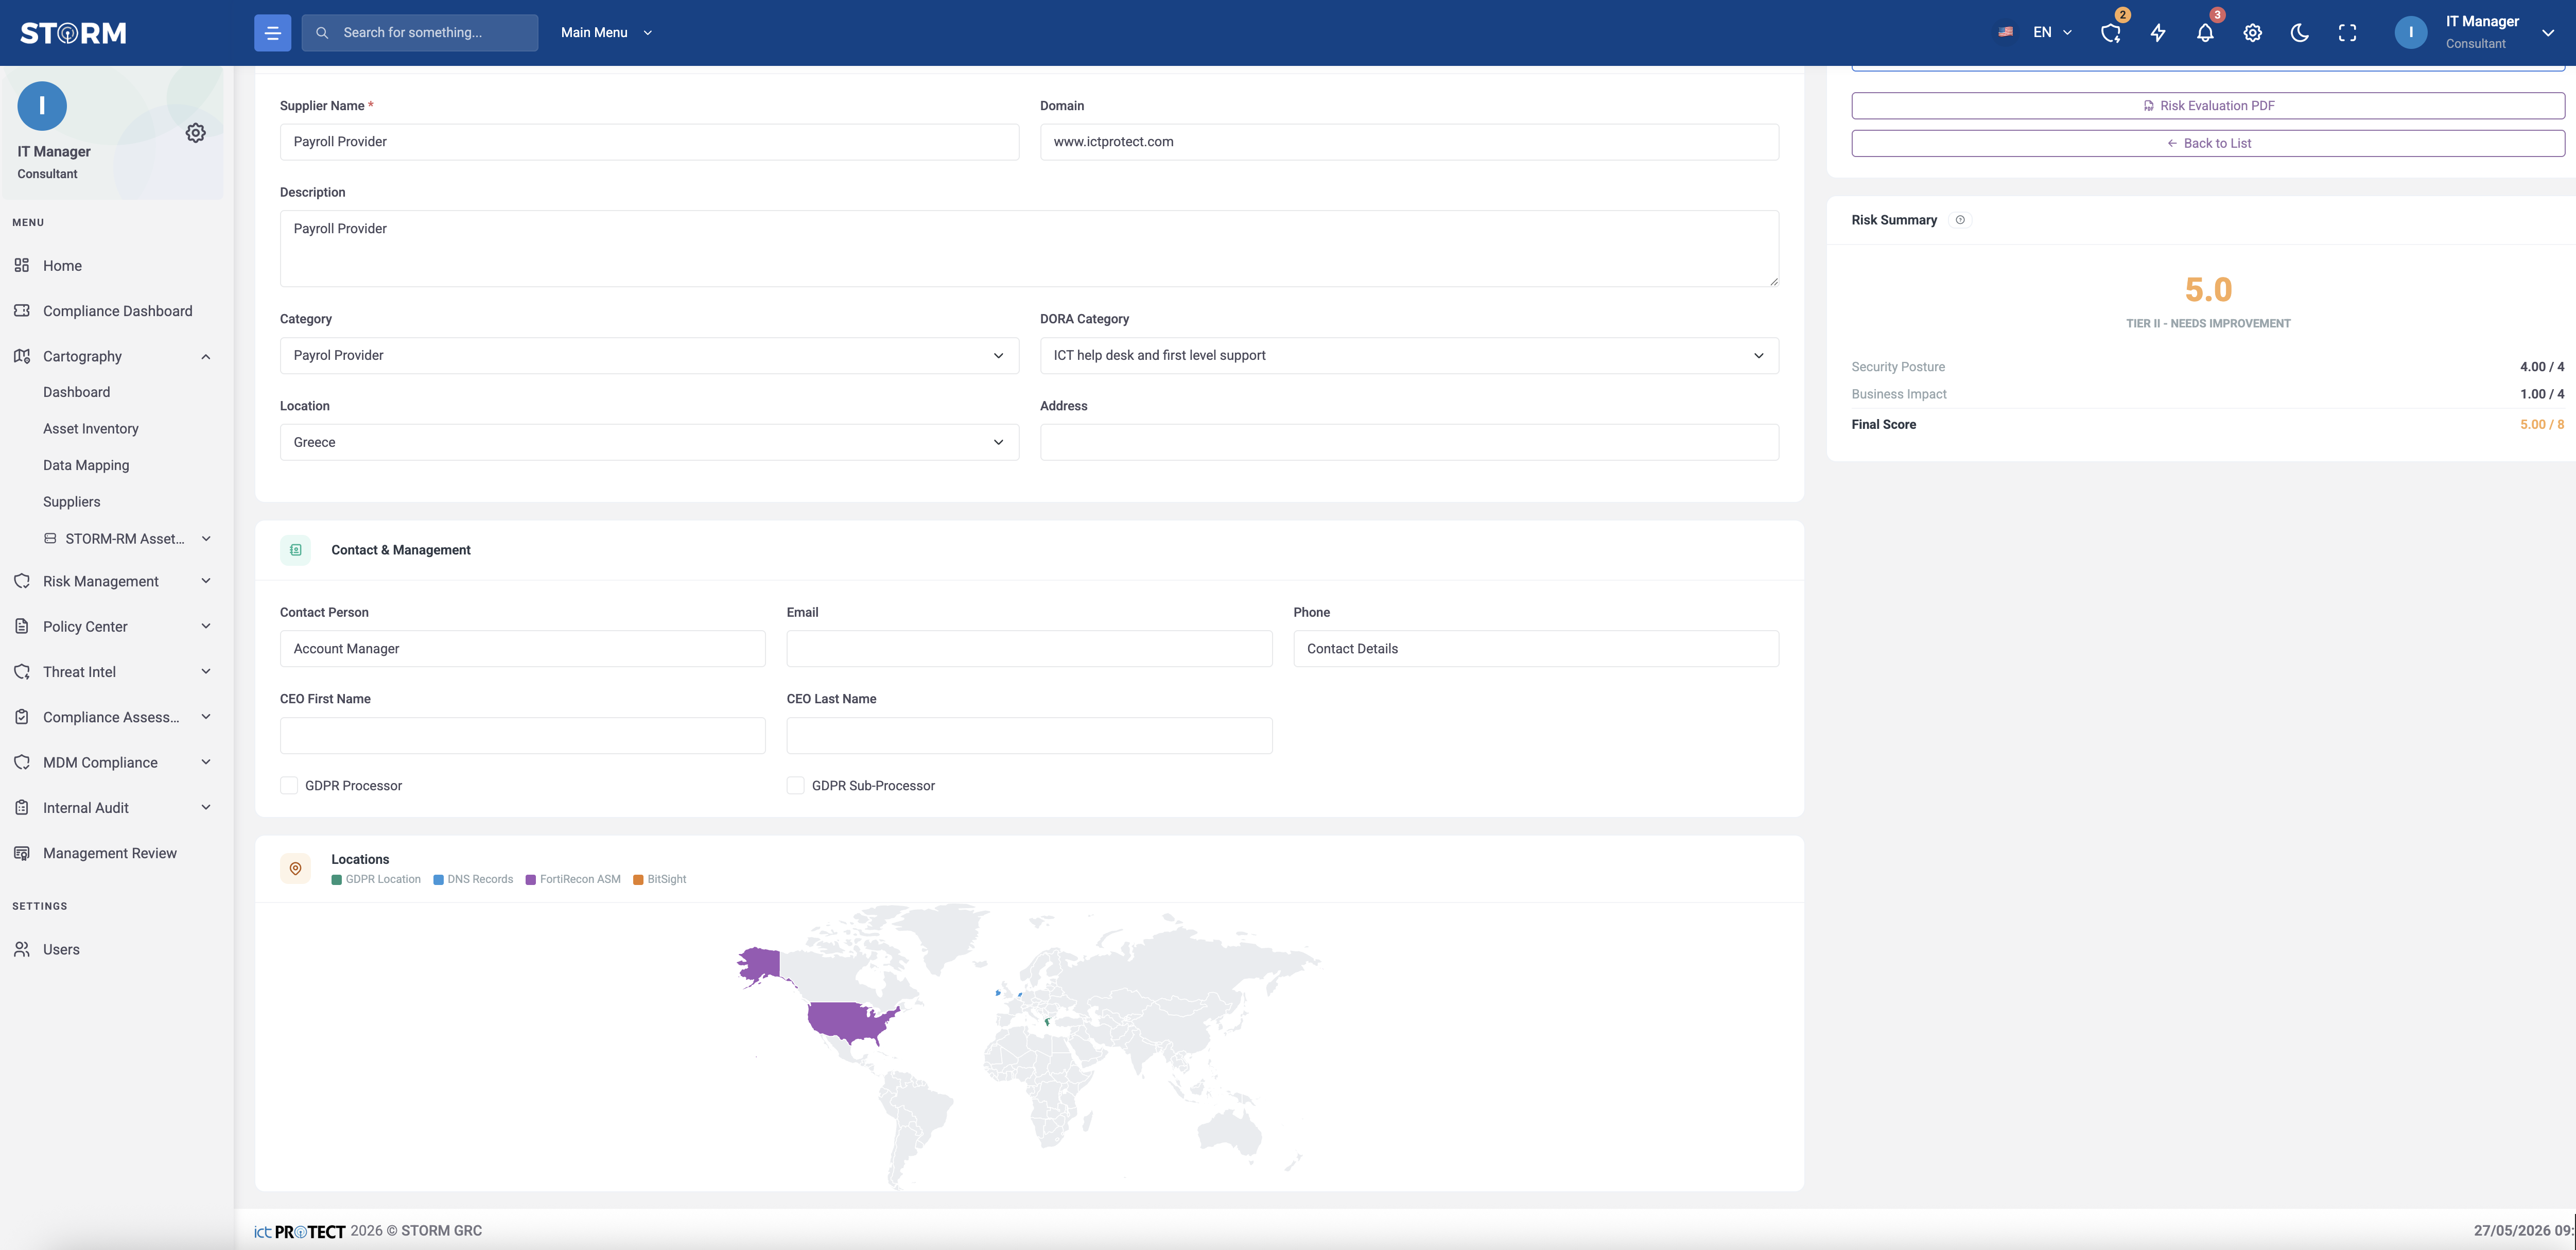
STORM combines supplier inventory, configurable questionnaires, evidence uploads, implementation status and remediation tracking. That supports automotive supplier oversight without claiming a preconfigured VDA ISA questionnaire.
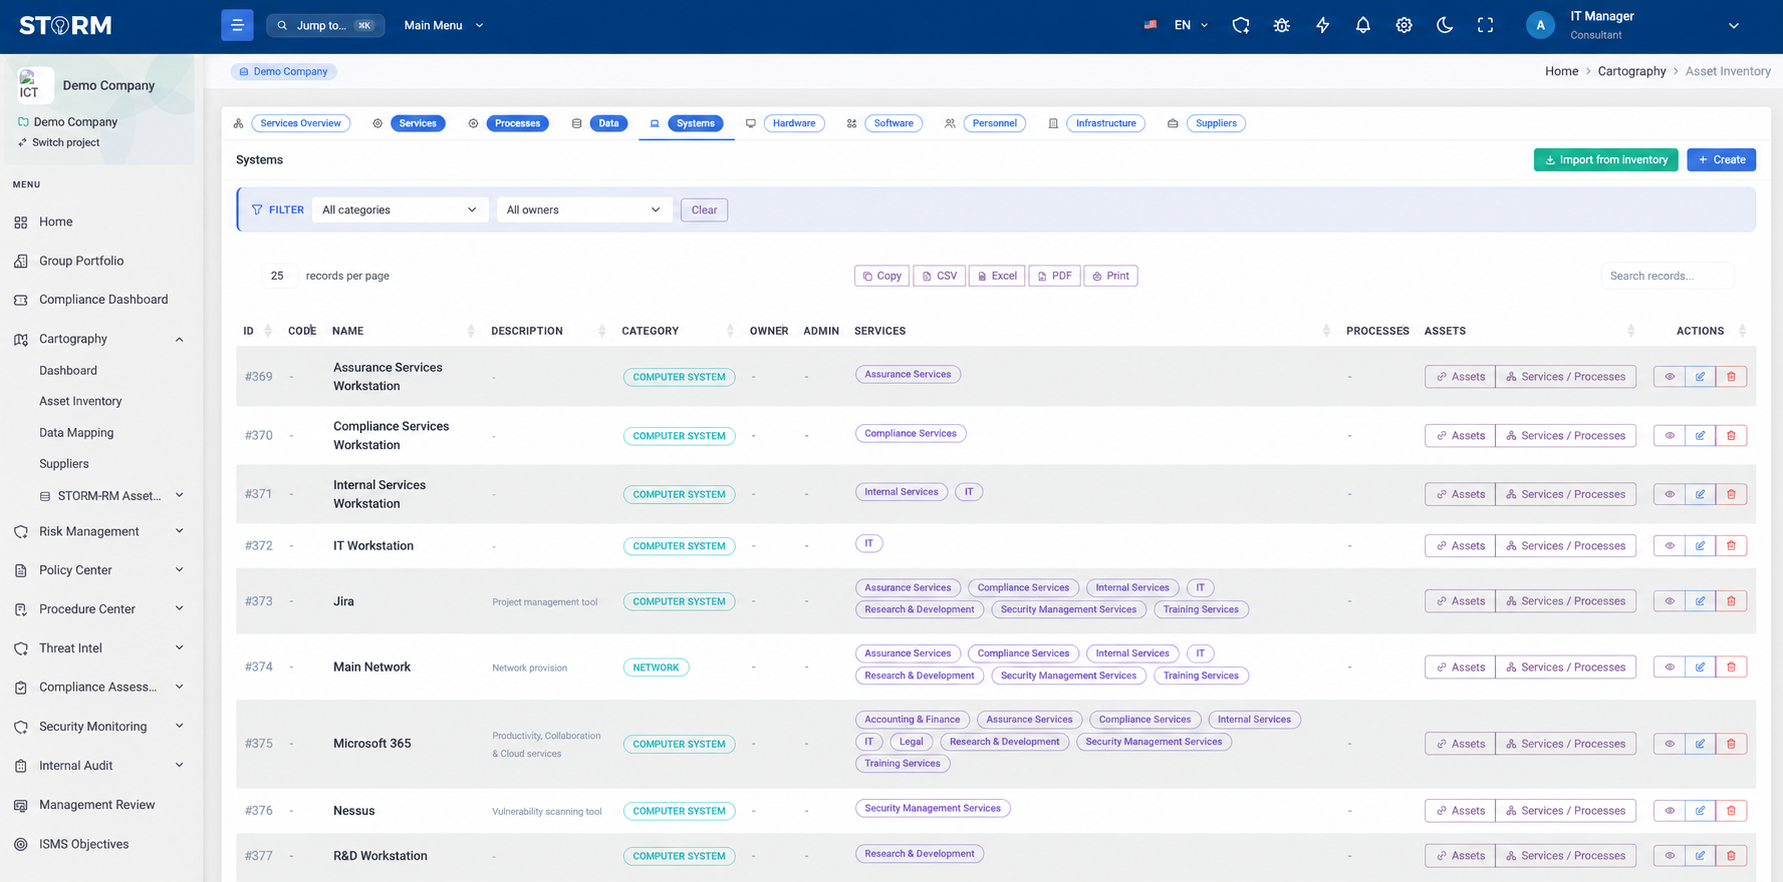
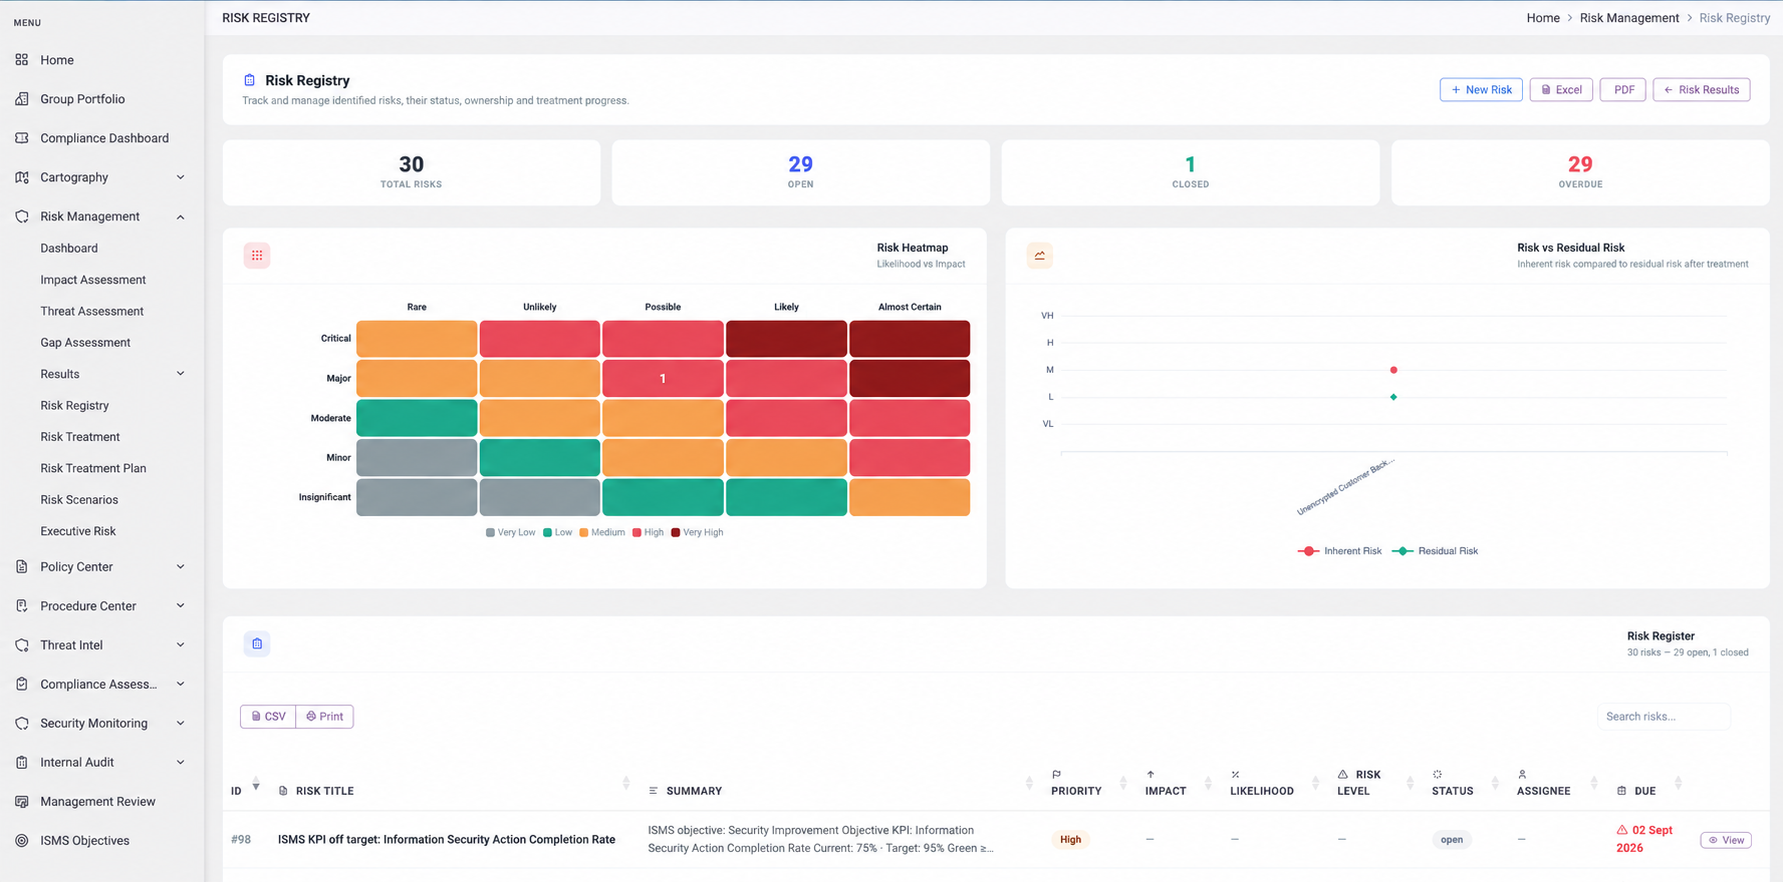
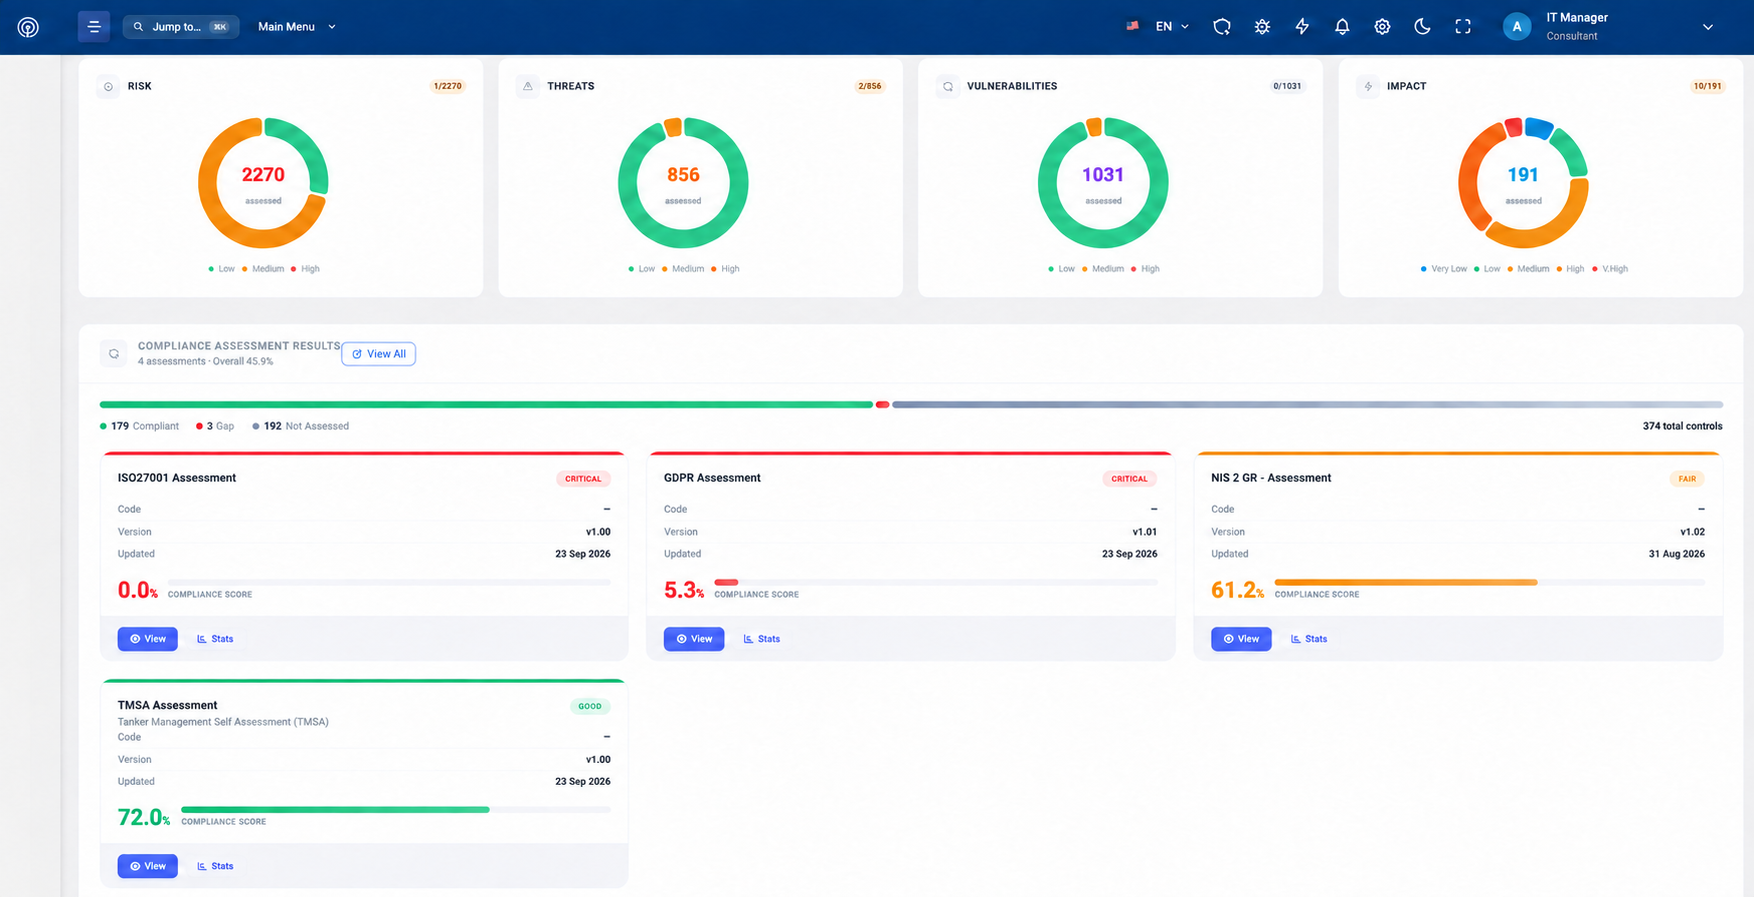
Cartography gives teams a reusable view of assets, operations and third parties. Findings can then be managed as risks with treatments, owners, due dates and attachments instead of remaining isolated questionnaire answers.
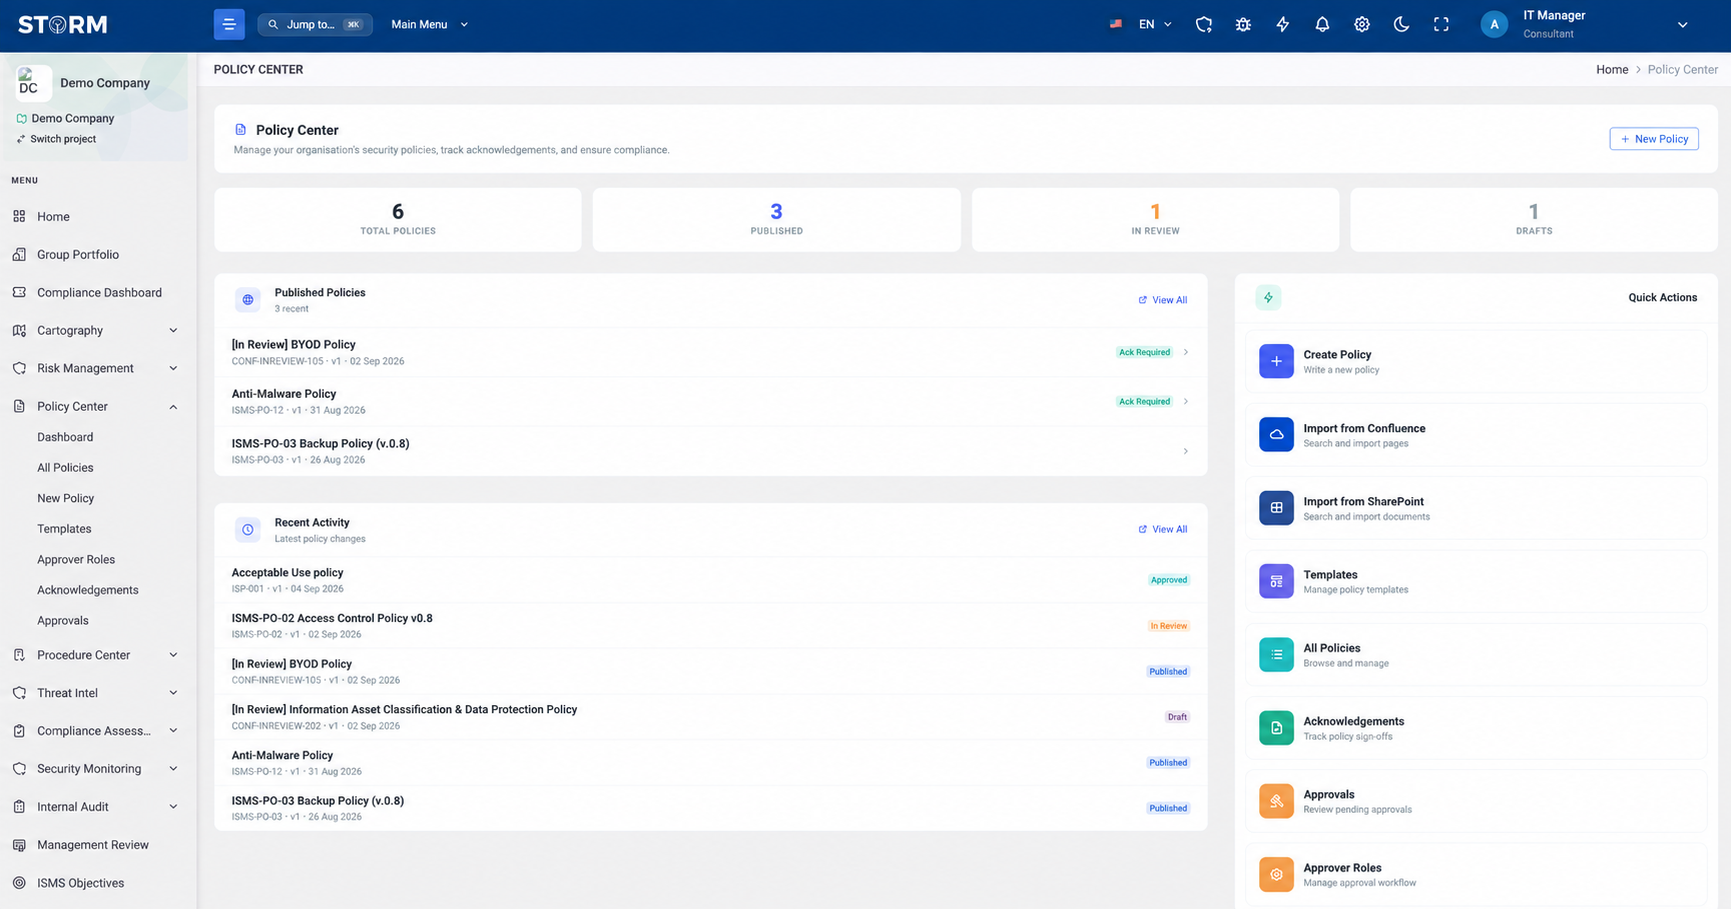
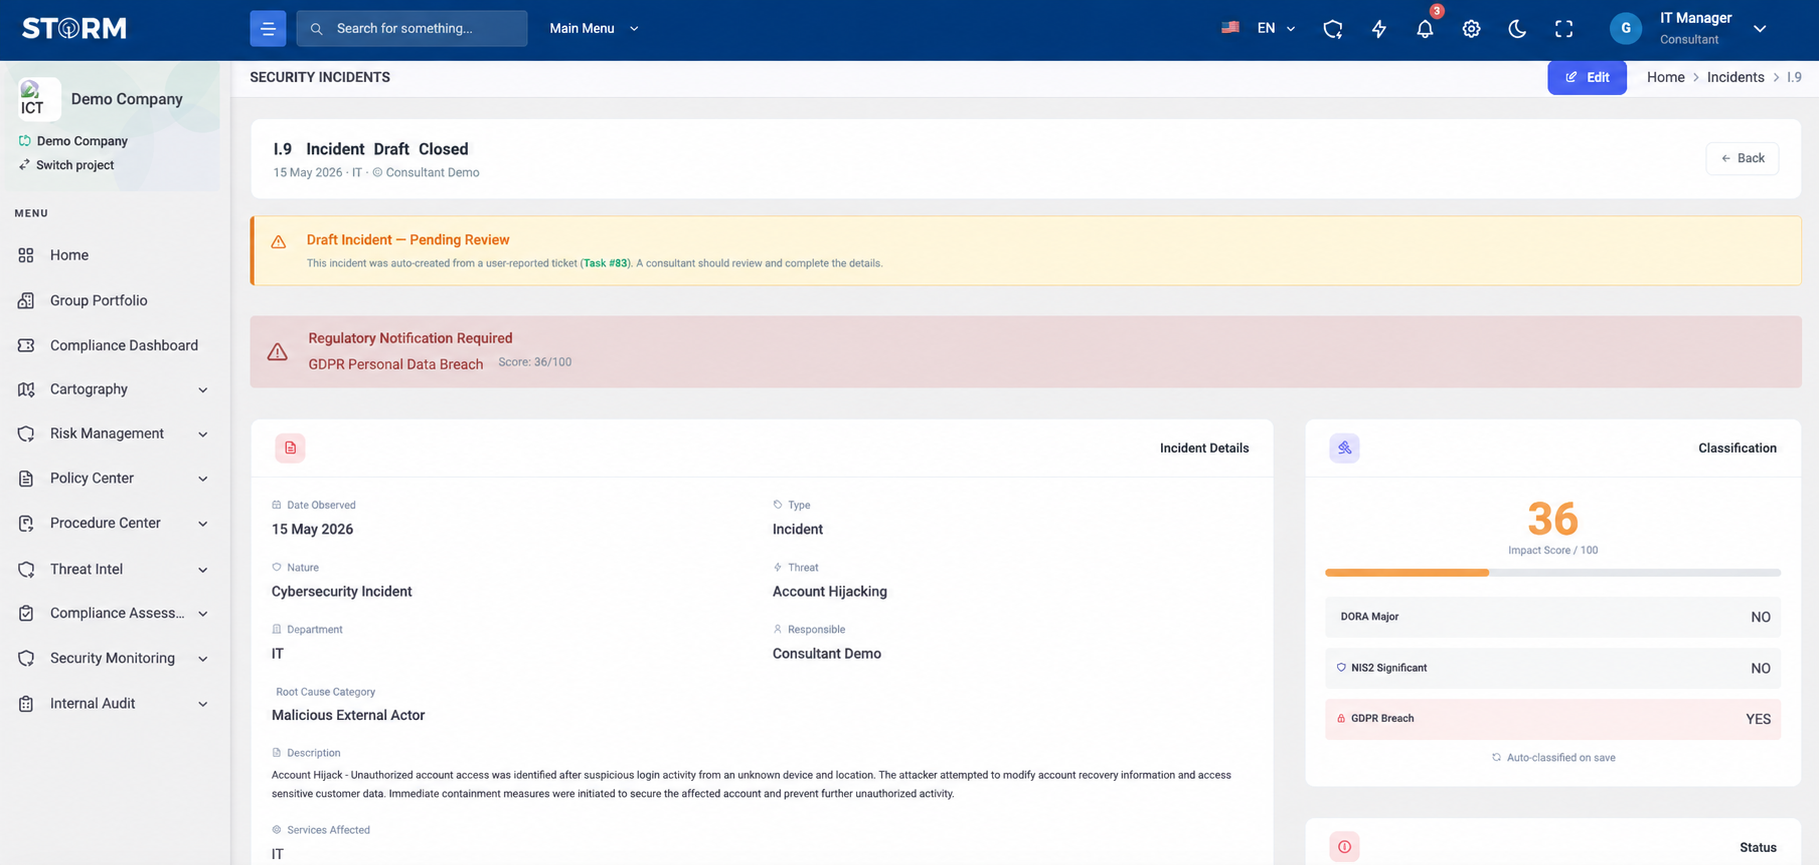
Controlled documents, incident records, internal audit findings and management reviews support the evidence trail behind security operations. Qualified teams and approved TISAX audit providers remain responsible for assessment conclusions.
The official materials separate the ISA catalogue from the TISAX assessment and result-sharing mechanism.
The core catalogue addresses a shared baseline for information and cybersecurity management across the automotive ecosystem.
ISMS · safeguards · maturityApplicable objectives bring in requirements for protected parts, vehicles, test vehicles and prototype-related events.
Physical · organisational · handlingApplicable objectives address processor activities involving personal data and special categories under the GDPR context.
Processor · personal data · evidenceRegistration, scope, self-assessment, independent assessment, corrective action and controlled result exchange sit around the catalogue.
ENX · audit provider · labelsThese summaries do not reproduce the official ISA questions or requirements. Use the applicable official catalogue and the ENX Participant Handbook when defining assessment scope and objectives.
STORM can organise readiness work; TISAX registration, assessment and labels follow the official ENX process.
Confirm locations, scope, partner expectations, protection needs and assessment objectives.
Scope · objectivesUse the applicable official ISA content to evaluate implementation and assemble supporting evidence.
Self-assessment · evidenceConvert gaps into owned actions, risks, policy changes and retained proof of completion.
Findings · treatment · ownersWork with an approved audit provider and share resulting labels through the ENX Portal as authorised.
Independent assessment · exchangeClear boundaries make the page more credible for automotive buyers and audit teams.
Walk through your sites, suppliers, assessment objectives, policies, risks, evidence and remediation needs—and identify the official ISA content that must be configured.