One GRC platform. Every framework your auditor names.

STORM GRC unifies compliance, risk, audit, incidents, suppliers, BCP and policies on a single platform — built around a methodology refined over more than a decade, and integrated with the tools you already run.

15+Frameworks
12Modules
EUHosted
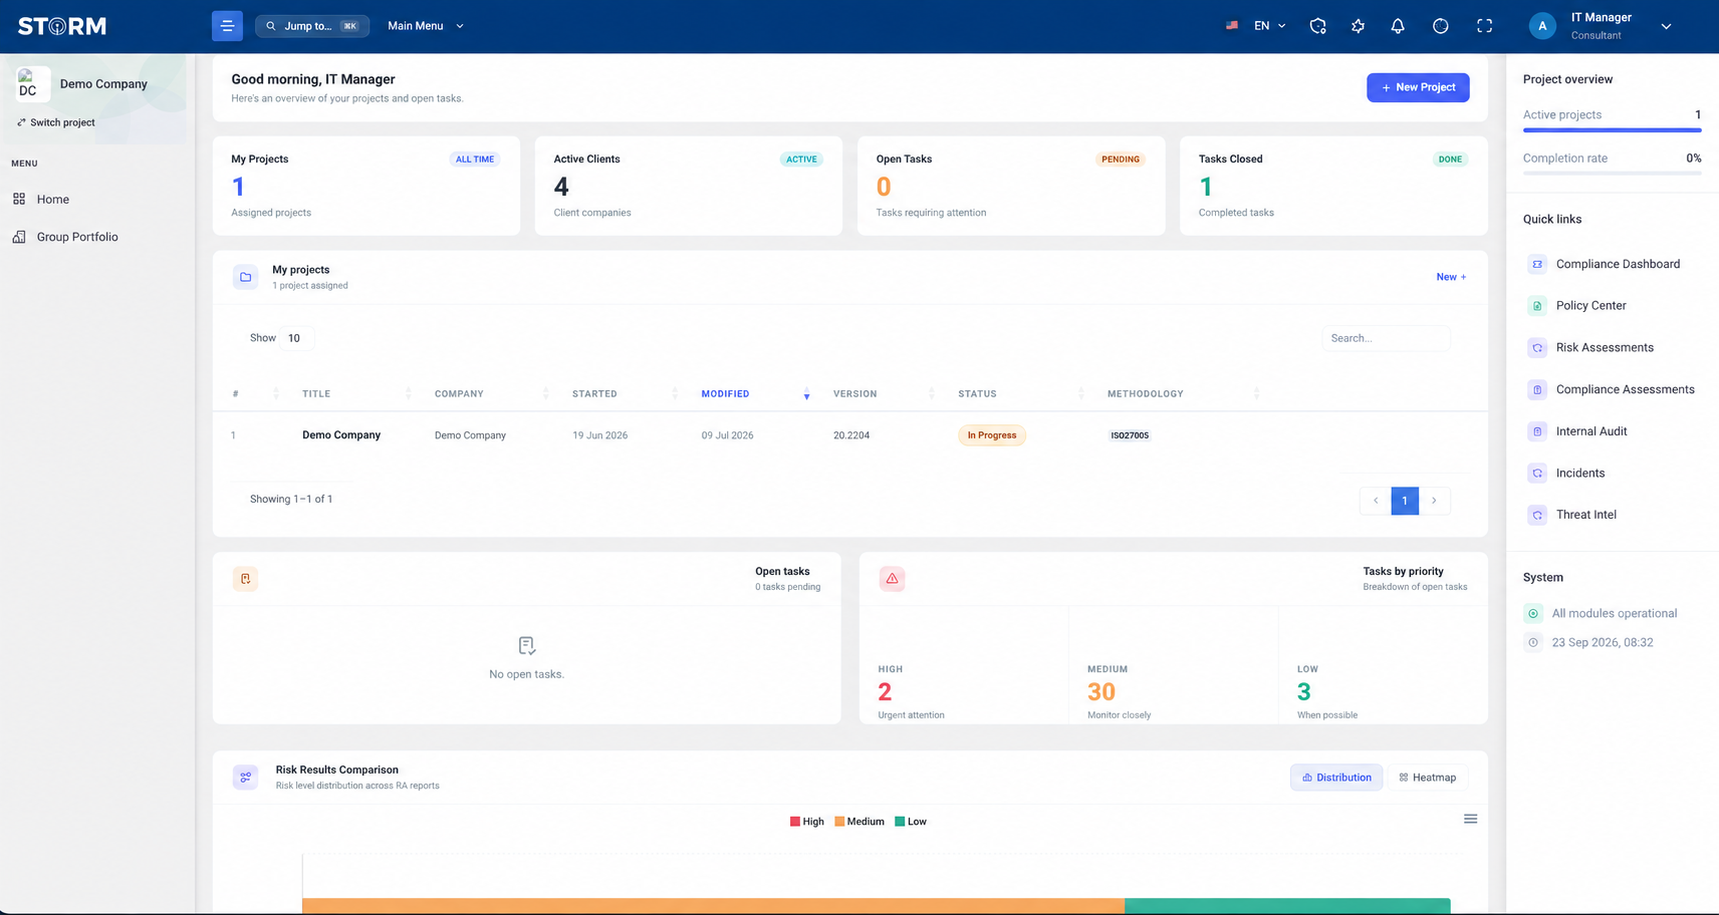
STORM home and project overview
Recognitions Independent awards for the STORM platform and its industry-specific implementations
Cyber Security Awards 2025 Gold
GoldMaritime cyber framework
Cyber Security Awards 2025 Silver – Integrated cyber services
SilverIntegrated cyber services
Cyber Security Awards 2025 Silver – GRC automation
SilverGRC automation
Compliance Awards 2025 Bronze – Best compliance platform
BronzeBest compliance platform
Cyber Security Awards 2026 Silver – Best Project
Silver 2026Best Project – New Product (Risk Analysis)
Cyber Security Awards 2026 Silver – Best Use of Risk Technology
Silver 2026Best Use of Risk Technology & Platform
Cyber Security Awards 2026 Silver – Best Cybersecurity Risk Management
Silver 2026Best Cybersecurity Risk Management
Trusted by security and compliance teams across regulated industries
Banking
Maritime
Energy
Critical Infrastructure
Cloud
Software
Pre-mapped to the frameworks regulators actually write.
15+ frameworks · cross-mapped
ISO/IEC 27001Information security
ISO 22301Business continuity
ISO/IEC 27017Cloud security controls
ISO/IEC 27018Public cloud privacy
ISO/IEC 27019Energy utility security
ISO/IEC 27701Privacy management
ISO/IEC 42001AI management systems
NIST CSFCybersecurity framework
SOC 2Audit-ready controls
GDPREU personal data
NIS2Network resilience
DORADigital resilience
NERC CIPCritical infrastructure
VDA ISAAutomotive security
IMO MSC.428(98)Maritime cyber risk
TMSATanker safety management
DryBMSDry bulk management

ISO/IEC 27001Information security
ISO 22301Business continuity
ISO/IEC 27017Cloud security controls
ISO/IEC 27018Public cloud privacy
ISO/IEC 27019Energy utility security
ISO/IEC 27701Privacy management
ISO/IEC 42001AI management systems
NIST CSFCybersecurity framework
SOC 2Audit-ready controls
GDPREU personal data
NIS2Network resilience
DORADigital resilience
NERC CIPCritical infrastructure
VDA ISAAutomotive security
IMO MSC.428(98)Maritime cyber risk
TMSATanker safety management
DryBMSDry bulk management
Product tour

The workspace your team will live in.

Explore the core STORM workspace: asset model, risk results, data mapping, treatment plans, dashboards, incidents and the risk registry.

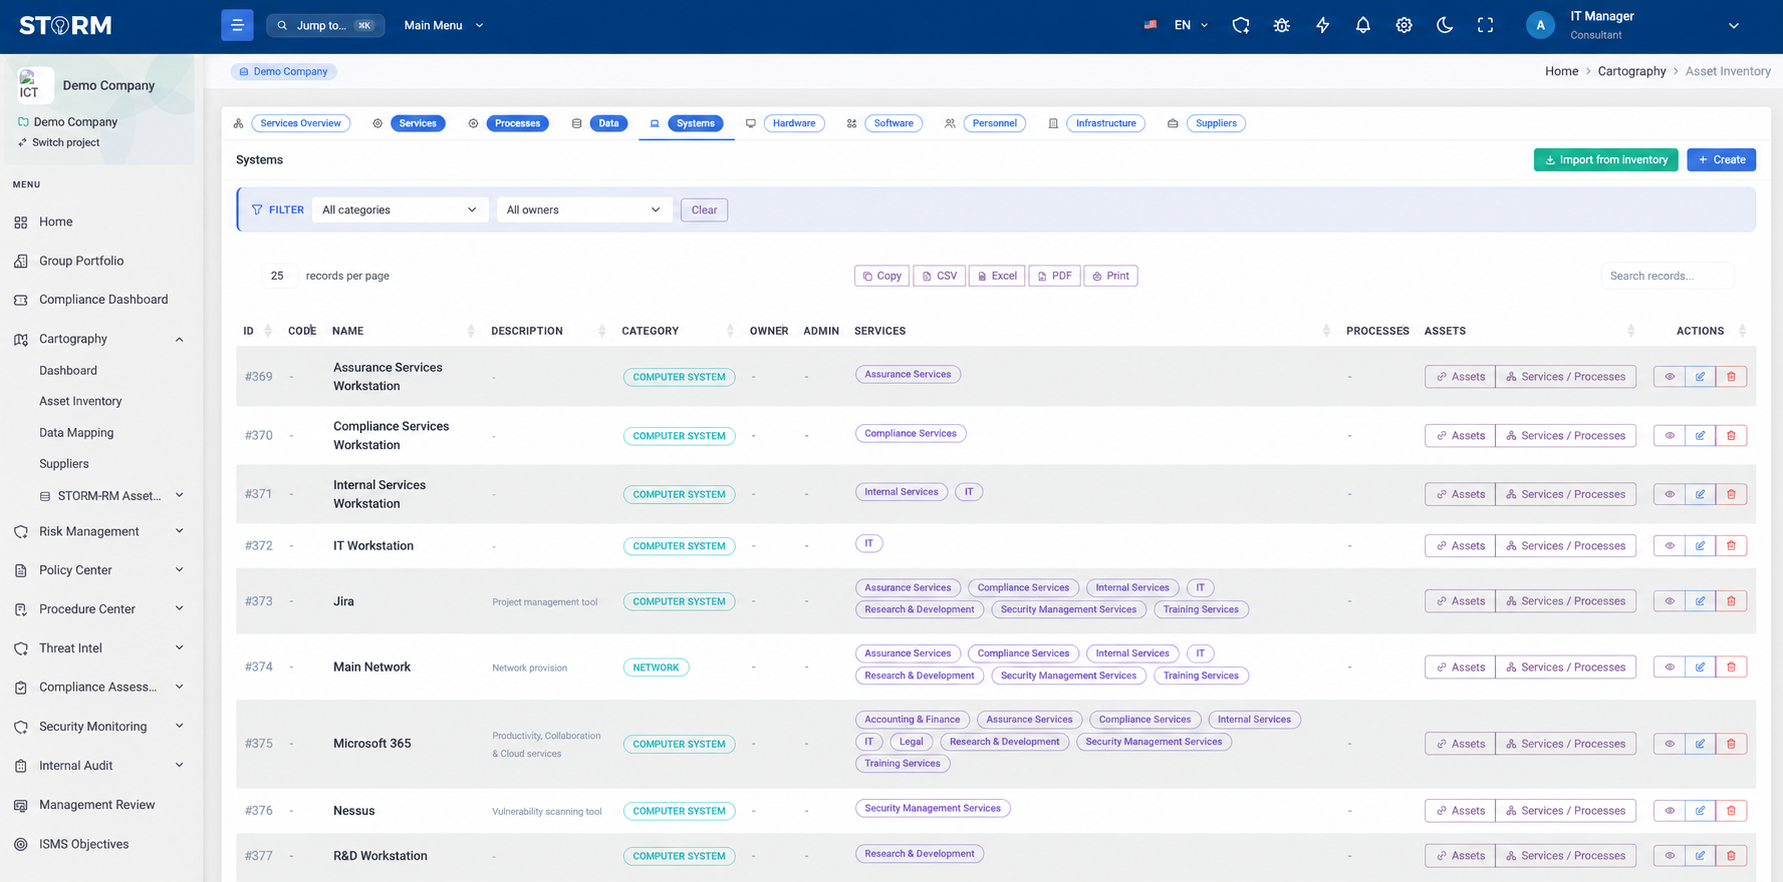
STORM Asset Model interface showing systems, services and dependencies
Why STORM GRC

STORM GRC platform replaces spreadsheets, disconnected tools, and manual processes.

Unified Platform

Manage all GRC activities from one dashboard — compliance, risk, audit, incidents, suppliers, and business continuity.

Multi-Framework Support

ISO 27001, NIST CSF, SOC 2, DORA, NIS2, GDPR, NERC CIP, VDA ISA and more — with cross-mapping between frameworks.

Actionable Intelligence

Real-time dashboards, automated risk scoring, threat intelligence feeds, and BitSight security ratings integration.

Audit-Ready Reports

One-click PDF generation for compliance assessments, risk reports, gap analyses, and audit findings — always audit-ready.

15+Compliance Frameworks
100%Audit Trail
Real-TimeRisk Dashboards
One-ClickReporting
AutomatedIntegrations
GRC architecture

Five phases. One defensible methodology.

STORM is built around a five-phase GRC model that maps end-to-end from asset cartography to compliance monitoring. Each phase is a working module, but the value comes from the data flowing between them.

PHASE 01
Cartography
Information assets & dependencies.
Asset inventory with classification and dependency mapping.
Business Impact Analysis.
BIA across business activities with RTO and RPO targets.
Records of Processing Activities.
GDPR Article 30 register, maintained in the same workspace.
PHASE 02
Risk Management
Threat & vulnerability assessment.
Maintained libraries mapped to your applicable frameworks.
Risk mitigation.
Pre-defined security controls applied per risk and per framework.
Overall risk register.
Identify, evaluate and manage the organisation's residual risk.
PHASE 03
Policies & Procedures
Policy & procedure development.
Security policies, BCP, DRP and training material in one editor.
Workflow approval.
Implement procedures via draft → review → approved → archived workflow.
Incident management.
Reporting, classification, response and analytics — integrated.
PHASE 04
Third-Party Risk
Critical supplier identification.
Classify suppliers by dependency and risk exposure.
Third-party security assessments.
Questionnaires, evidence, and tiered reviews.
External ratings.
BitSight and FortiRecon ratings integrated directly into the supplier file.
PHASE 05
Compliance Monitoring
Internal audits.
Conduct audits against your applicable security standards.
Roles & collaboration.
Assign responsibilities and enhance cross-team collaboration.
Corrective actions.
Monitor remediation and non-conformity closure to deadline.
Integrations

Your security stack, connected to your GRC.

STORM connects to the security, supplier-risk and collaboration tools you already run. It turns their data into control status, risk and supplier context, then routes the follow-up to the people who own it, so audit evidence keeps itself current.

01 Security configuration

Microsoft security & cloud

  • Entra ID
  • Intune
  • Defender
  • Azure
  • Sentinel
  • Microsoft 365
What comes in
Identity, device, security and cloud configuration data, collected, analyzed and mapped to STORM controls.
What you get
Automated checks such as MFA enforcement and device encryption, evaluated against your thresholds. Results update control status, map to ISO/IEC 27001 and other supported frameworks, and pre-fill evidence in compliance assessments.
Continuous Monitoring
02 Vulnerability findings

Scanners & security tools

  • Tenable Nessus
  • Microsoft Defender
  • Spreadsheet import
What comes in
Findings from vulnerability scanners, plus penetration-test results imported from a template.
What you get
One view of every finding, linked to the affected asset, prioritised with CVSS and CISA KEV, and assigned to an owner with SLA tracking.
Vulnerability Management
03 External risk signals

Threat & supplier intelligence

  • FortiRecon
  • BitSight
What comes in
Dark-web, leaked-credential and breach intelligence from FortiRecon, and external security ratings from BitSight.
What you get
Outside-in signals on each supplier record, next to questionnaire answers and business impact, feeding the supplier's risk tier and your threat-intelligence view.
Third-Party Risk Management
04 Work & documents

Collaboration tools

  • Jira
  • Microsoft Teams
  • Email
  • SharePoint
  • Confluence
What comes in
Policies and procedures imported and kept in sync from SharePoint, and existing documentation imported from Confluence.
What goes out
Risk mitigation actions sync to Jira. Teams and email notify owners about tasks, reviews, approvals and policy acknowledgements.
Policy Management
Example · from configuration check to audit evidence
  1. CollectIntuneReports device encryption status
  2. EvaluateSTORM checkCompares the result with your threshold and severity
  3. MapFramework controlUpdates implementation status for the mapped control
  4. EvidenceCompliance assessmentPre-fills the response, with history kept for the auditor
Policy center & document management

Centralised policy lifecycle management.

Inside the editor

Rich Text Editor
Create and edit policies with a full editor, versioning, and approval workflows.
Version Control
Track every change with complete version history, diff comparison, and rollback.
Approval Workflow
Multi-level approval: draft → review → approved → archived lifecycle.
Framework Mapping
Link policies directly to specific framework controls for traceability.
Confluence & SharePoint
Bi-directional synchronisation with your existing knowledge base.
PDF Export
Professional policy documents with cover pages, table of contents and branding.
UnlimitedPolicies
FullVersion History
Multi-LevelApprovals
AutoCompliance Mapping
Compliance & gap analysis

Score every control. See the gap. Close it.

Multi-framework assessments — ISO 27001, NIST CSF, SOC 2, DORA, NIS2, GDPR and more.
Automated compliance scoring with a 5-level maturity scale per control.
Visual heatmaps with drill-down to evidence and remediation.
Cross-framework control mapping — answer once, reuse across standards.
Policy & control linkage — every policy traces to a specific control.
Remediation tracking with task assignment and deadlines.
One-click PDF / Word / Excel / PPT compliance reports for auditors and boards.

Compliance Score Scale

ExcellentVL
GoodL
FairM
PoorH
FailedVH

STORM helps teams centralize governance, risk, compliance and operational security workflows in one workspace — improving audit readiness and reducing manual coordination.

↓
Reduced manual effort Less administrative overhead during audit preparation
✓
Unified workflows Risk, asset, incident and treatment management in one platform
→
Faster visibility Clearer onboarding across security and compliance operations
Frequently asked

Answers, before you ask.

The questions security and procurement teams ask us most often before a demo.

Is STORM available cloud or on-premise?
STORM is delivered as a managed SaaS solution, hosted in EU-certified data centers. For enterprises in critical infrastructure sectors with strict data locality requirements, on-premise deployment can be discussed.
How does the MDM and EDR integrations work?
STORM pulls endpoint posture, configuration state and asset attributes from your MDM and EDR via supported APIs. The data pre-populates the risk assessment, supplies control evidence during audits, and maps automatically to the relevant security standard control (e.g. ISO 27001 A.8.1). You still review and sign off — STORM doesn't fabricate evidence.
How long does implementation take?
A typical SME has its asset inventory and risk register live within two weeks. A full ISO 27001 readiness path — policies, SoA, risk treatment, internal audit — runs 60 to 90 days. Larger operators with multiple sites, frameworks or fleets plan 90 to 180 days.
How is STORM priced?
STORM is licensed per organisation, scaled by user count, site/fleet count and the frameworks you need. There are no per-document or per-report fees. We send a fixed quote after a 30-minute scoping call so you know the year-one cost up front.
Which frameworks are supported out-of-the-box?
ISO 27001, ISO 22301, NIST CSF, SOC 2, GDPR, NIS2, DORA, NERC CIP, VDA ISA and IMO MSC.428(98) — with cross-mapping between them. Additional frameworks (IEC 62443, ISO 27017/27018, TISAX, sector circulars) are added on customer request.
Where is the data hosted?
SaaS customer environments are hosted in EU-based data centers under EU jurisdiction. Our hosting infrastructure is certified and operated in accordance with globally recognized standards and best practices, including ISO 27001, ISO 22301, and SOC 2 Type II.

Does STORM integrate with Jira, Teams and Confluence?
Yes. Remediation tasks and audit findings sync to Jira and Microsoft Teams. Policies sync bi-directionally with Confluence and SharePoint, so your knowledge base stays in step with the approved control set.
Certifications

ICT PROTECT holds internationally recognised certifications across quality, security and assurance.

ISO 9001 · ISO 27001 · ISO 22301 · ISO 27701 ISAE 3000 Type I Cyber Essentials Certified and Cyber Essentials Plus
Get started

See STORM running on your frameworks.

A 30-minute screen-share with a STORM specialist. We map your current state to the frameworks that apply, show the integrations live against your stack, and you leave with a written gap summary — whether you buy or not.

Book a 30-min demo

No sales pressure. EU-based team.