
See the landscape
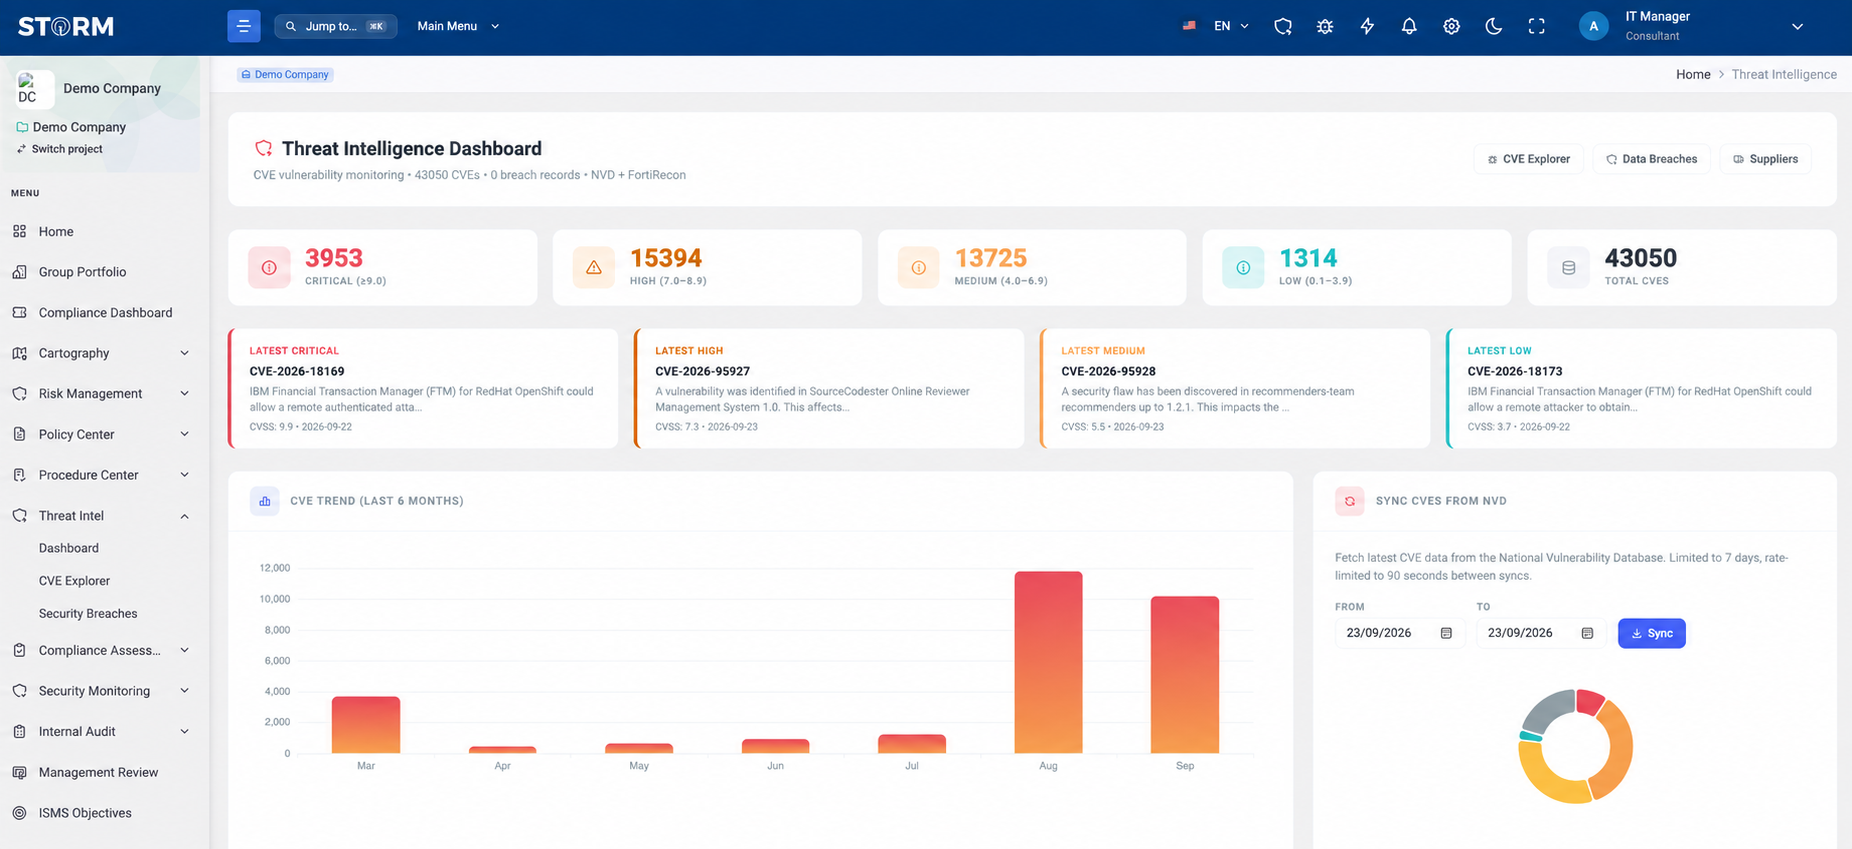
Use a centralized dashboard for vulnerability trends, severity distribution and key metrics.
Explore emerging vulnerabilities, publicly disclosed breaches and supplier-related threat signals in one workspace—then use that visibility to support risk assessment and remediation decisions.
STORM documents periodic feed synchronisation—not guaranteed real-time streaming. Geographic breach filtering is explicitly documented for Greece; wider geographic coverage should be confirmed.
Public vulnerability and breach feeds generate more information than teams can use without a way to search, filter and place it in context. STORM centralizes those records and adds supplier, vendor, severity and geographic perspectives so security teams can investigate what deserves attention.
Use a centralized dashboard for vulnerability trends, severity distribution and key metrics.
Search vulnerability details and narrow results using documented attributes.
Monitor supplier breaches and vulnerabilities associated with specific vendors.
Use relevant intelligence to inform risk assessment and remediation activity.
The module combines dashboard visibility, detailed vulnerability exploration and breach intelligence without presenting every external signal as an internal finding.
Bring periodically synchronized CVE data and disclosed breach intelligence into a single dashboard. Review vulnerability volumes, severity distribution, recent records and trend metrics before moving into detailed investigation.
Search and review CVE details, then filter by publication date, severity, CVSS score, vendor, product and other available attributes. The result is an investigation view, not a claim that every published CVE affects the organization.
Review publicly disclosed incidents, identify breaches relevant to the organization or its region, and monitor supplier-related security incidents and vendor-specific vulnerabilities. STORM explicitly documents geographic filtering for Greece.
The documented FortiRecon integration retrieves external threat and breach intelligence—including dark-web exposure, leaked credentials and vendor or supply-chain risk signals—for use in Threat Intelligence and Third-Party Risk Management.
The documented module supports investigation and informed remediation; it does not claim autonomous response.
Periodic public-feed updates
CVE and breach records
Severity, vendor, product and date
Supplier and geographic context
Risk and remediation decisions
Threat-intelligence usefulness depends on feed scope, synchronization frequency and how signals move into the organization’s operational process.
Bring the vendors, suppliers, products and geographies that define relevance for your organization.
Validate the feed scope, filters, FortiRecon signals and investigation workflow against the external exposure questions that matter to your organization.