
Context & scope
Understand the organisation, interested parties and boundaries of the information security management system.
Connect scope, assets, risk decisions, controls, policies, evidence, audits, objectives and management reviews in one operating record built around the Plan–Do–Check–Act lifecycle.
STORM supports implementation, operation and evidence. Certification decisions belong to an independent accredited certification body.
ISO/IEC 27001 defines requirements for establishing, implementing, maintaining and continually improving an ISMS. The work spans Clauses 4–10, not only the Annex A control catalogue.
Understand the organisation, interested parties and boundaries of the information security management system.
Set policy, responsibilities and management commitment so the ISMS belongs to the organisation—not only the security team.
Address risks and opportunities, assess and treat information security risk, and define measurable objectives.
Maintain resources, competence, awareness, communication and controlled documented information.
Plan and control the processes needed to operate risk assessment, treatment and the wider ISMS.
Monitor and evaluate performance, perform internal audits and conduct documented management reviews.
Manage nonconformities and corrective action and continually improve ISMS suitability, adequacy and effectiveness.
Compare risk-determined controls with the reference set and document inclusion, implementation and exclusions in the Statement of Applicability.
STORM includes built-in ISO/IEC 27001 support and connects the records that teams otherwise reconstruct across spreadsheets, documents, ticketing tools and point-in-time assessments.
Map services, processes, data, hardware, software, users, locations and suppliers, including internal and external dependencies. Multi-company deployments preserve entity-level segregation with consolidated oversight.
Cartography · organisational scopeUse STORM-RM, ISO/IEC 27005 or a configurable methodology; connect impact, threats and vulnerabilities to treatment, acceptance, owners and the Statement of Applicability.
Risk register · treatment plan · SoADefine information security objectives and KPIs, set targets and Green/Amber/Red thresholds, assign owners and monitor current and historical performance.
Clause 6.2 · KPIs · trendsAuthor or import policies and procedures, manage version history, approvals, review schedules and acknowledgements, and map documents directly to compliance controls.
Policies · RBAC · audit trailConnect supplier assessments, vulnerabilities, incidents, technical findings and mitigation actions to the affected assets, risks and accountable teams.
Suppliers · incidents · remediationTrace requirements to policies, technical checks, attestations and evidence; manage internal audits and findings; consolidate results in documented management reviews.
Compliance · internal audit · Clause 9.3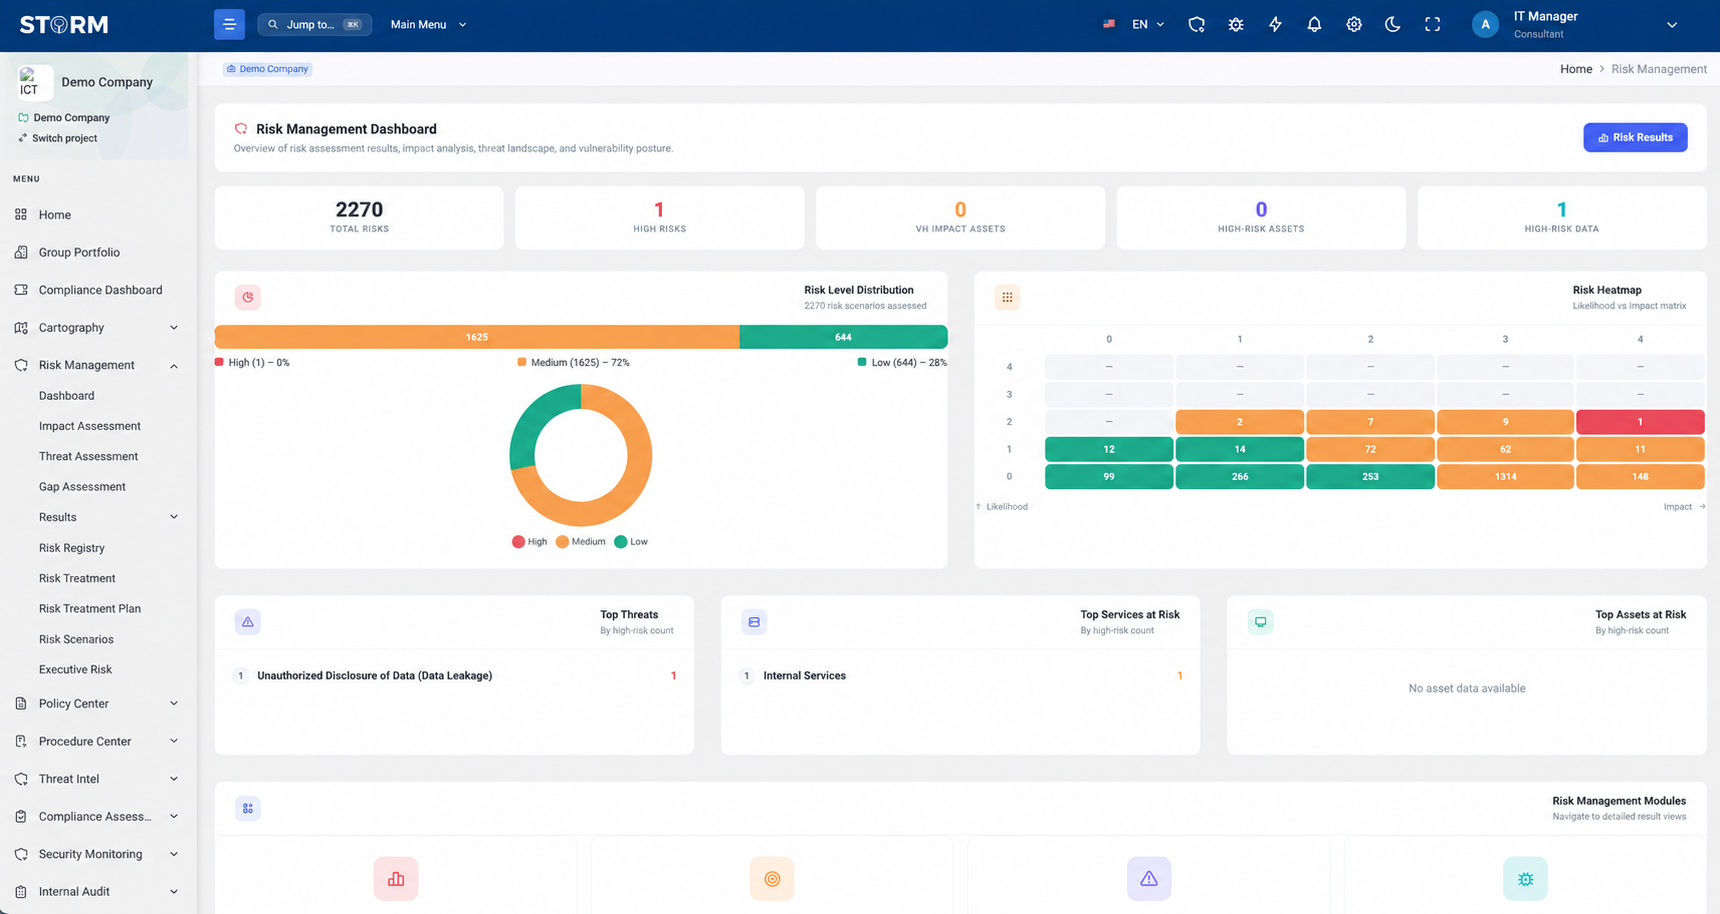
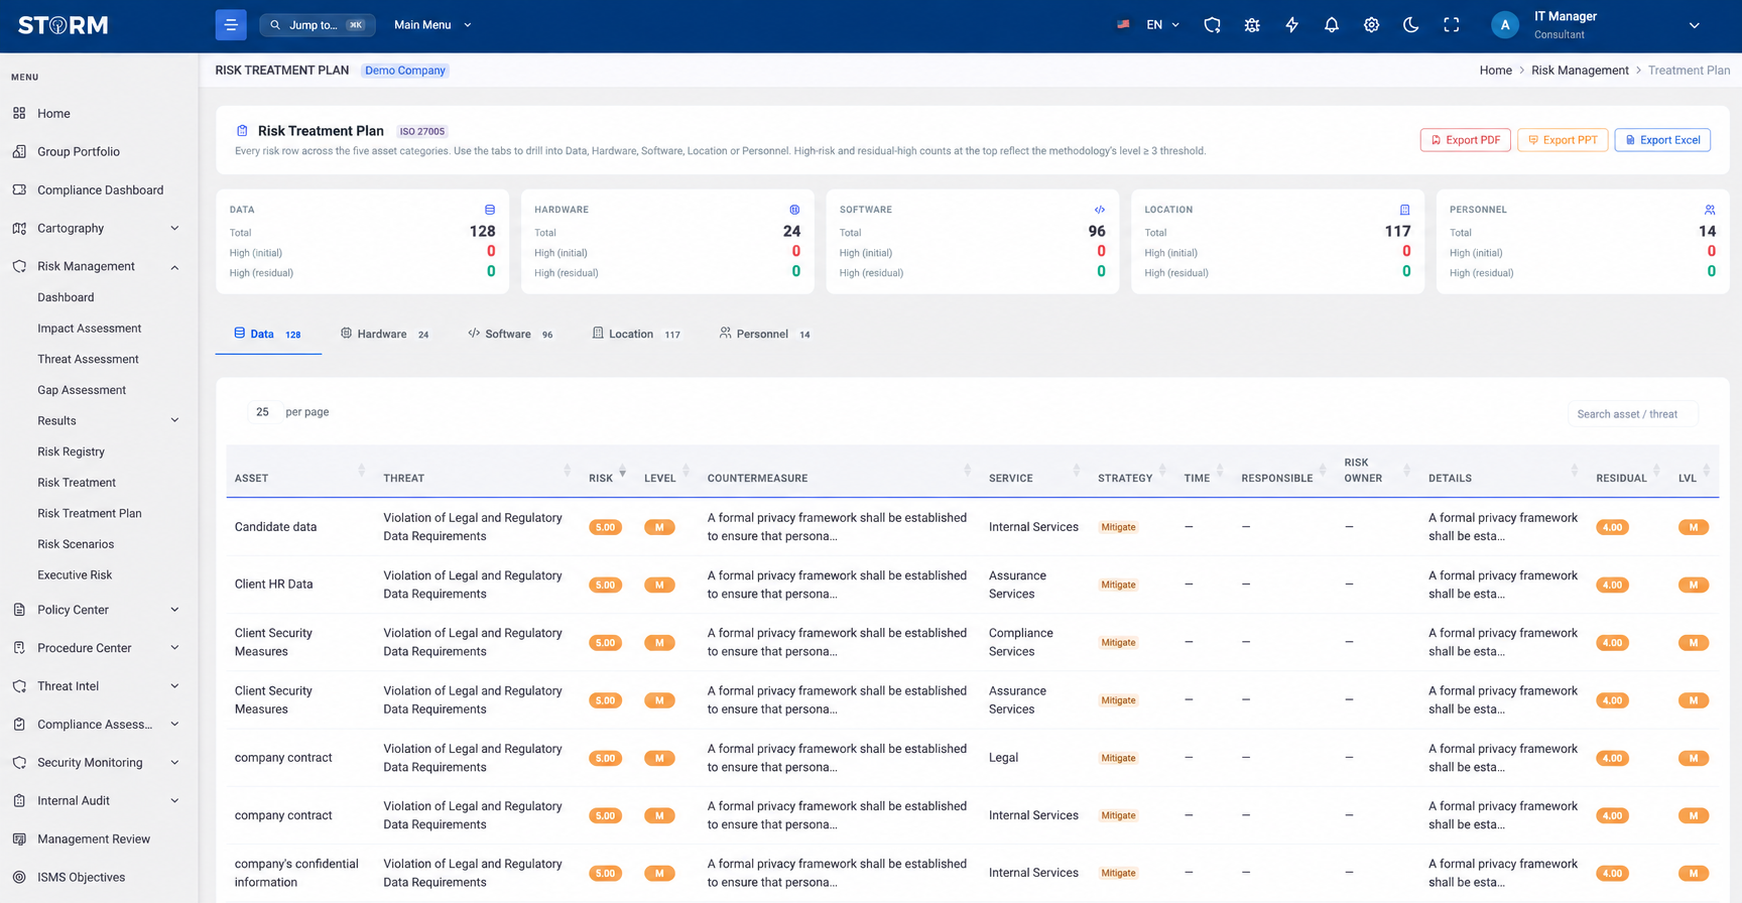
STORM turns asset context into impact, threat and vulnerability assessments, then carries those results into scenarios, risk levels, treatment decisions and a reviewable plan.
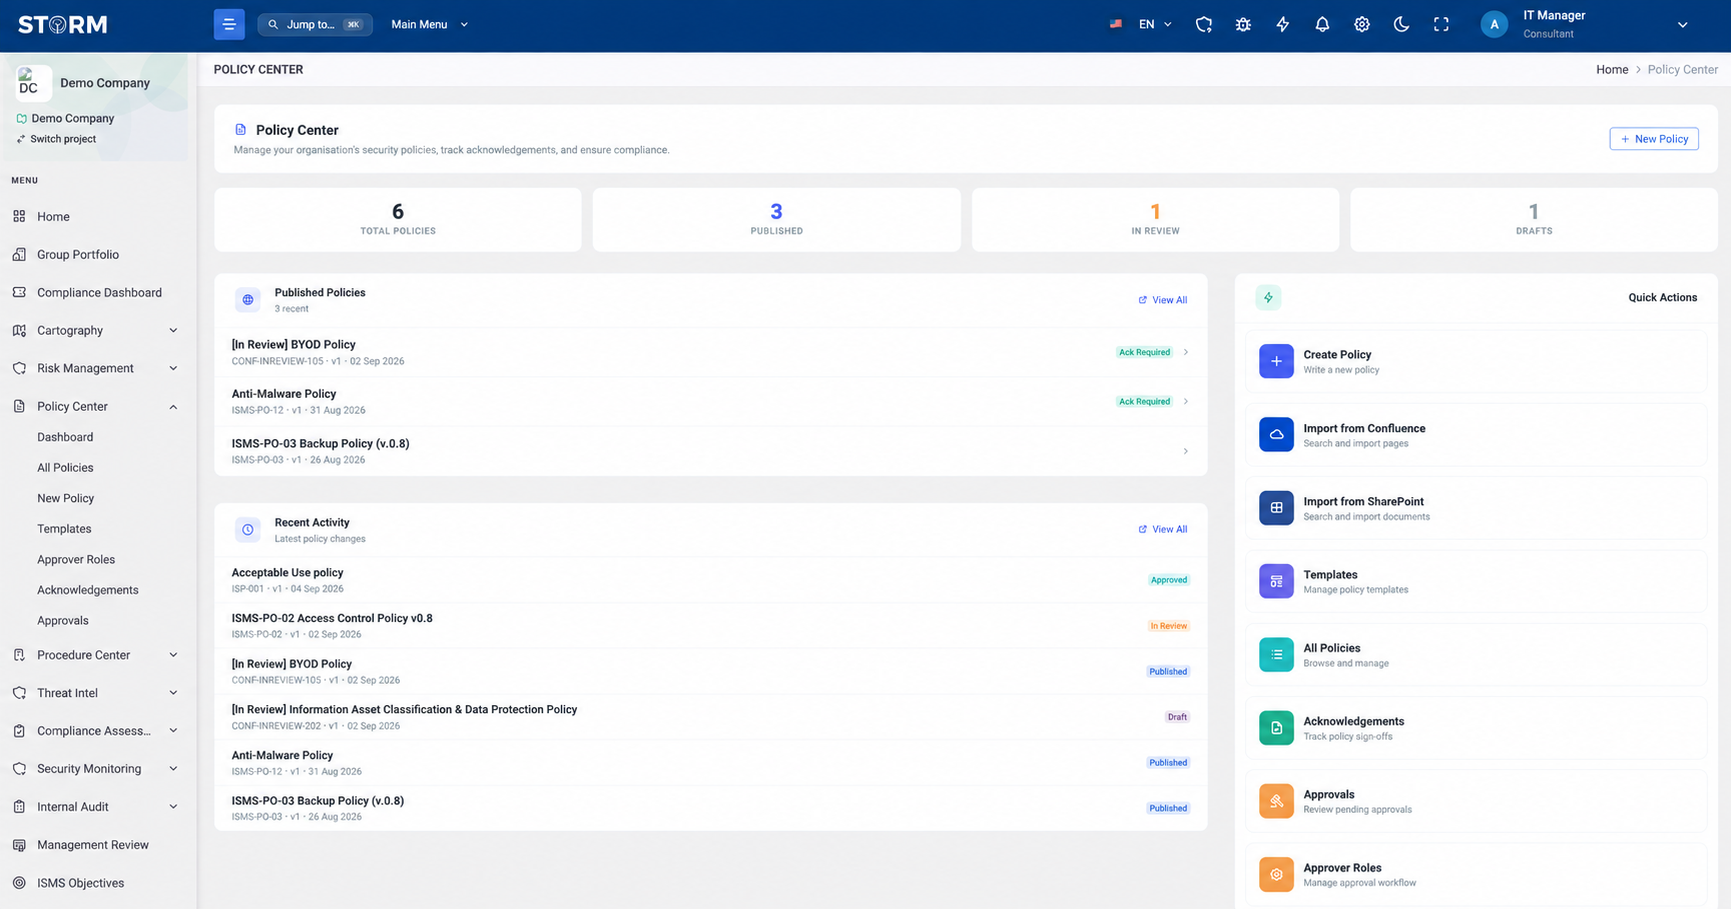
Policies and procedures retain their versions, owners, review and approval history, acknowledgement status and links to relevant controls. Existing content can be imported from SharePoint or Confluence.
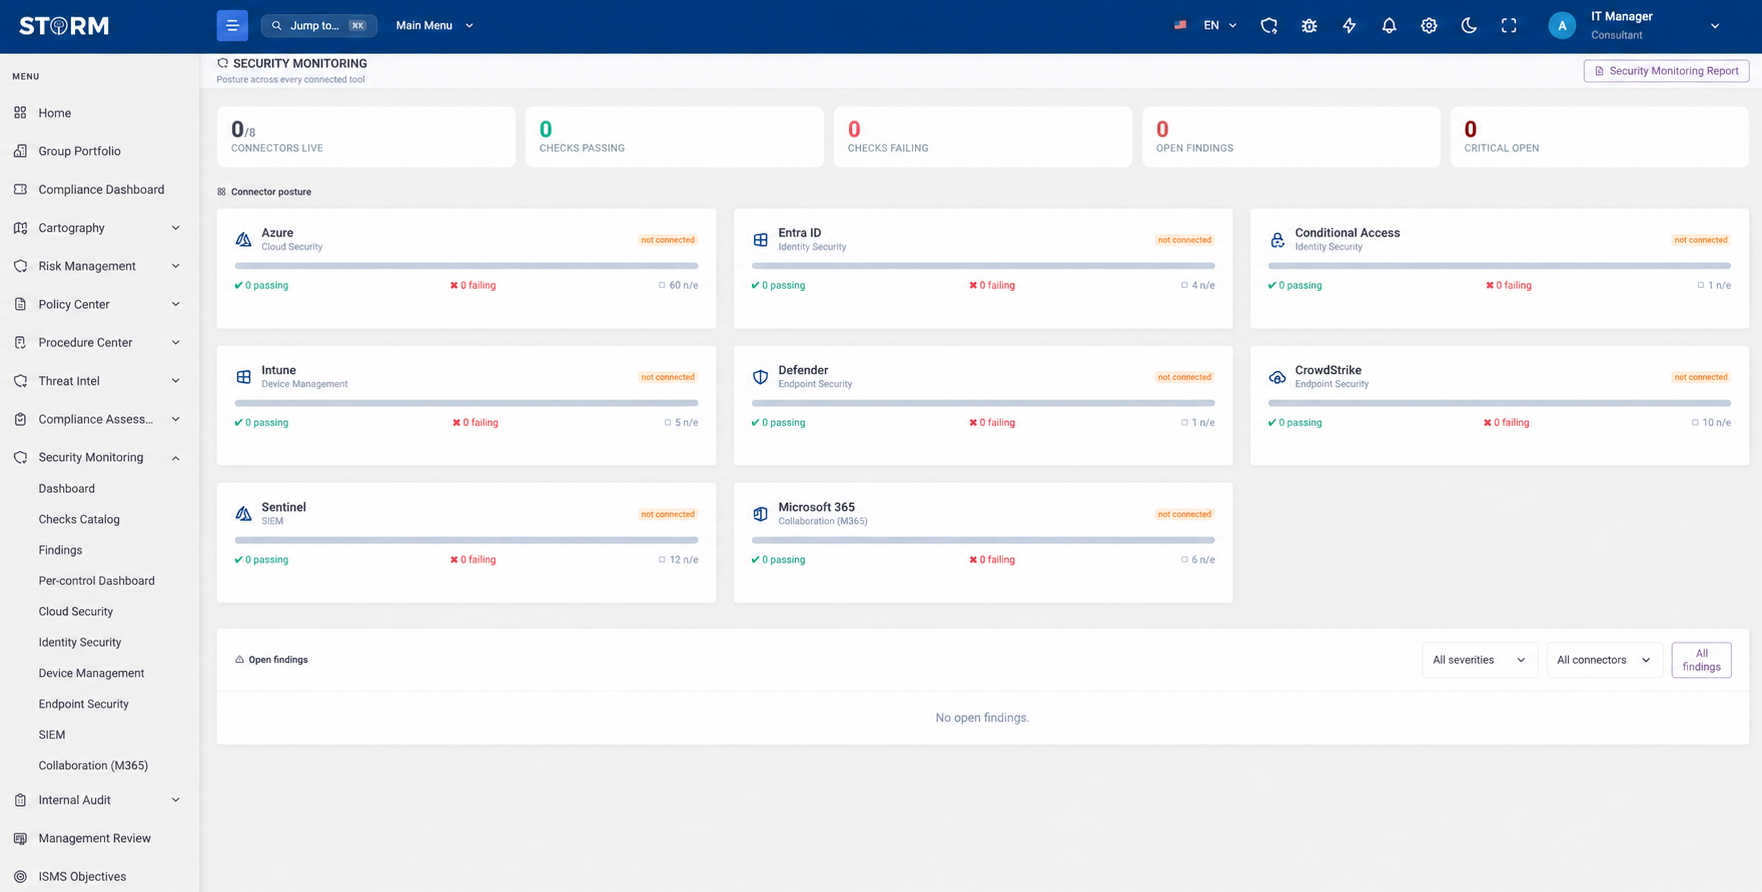
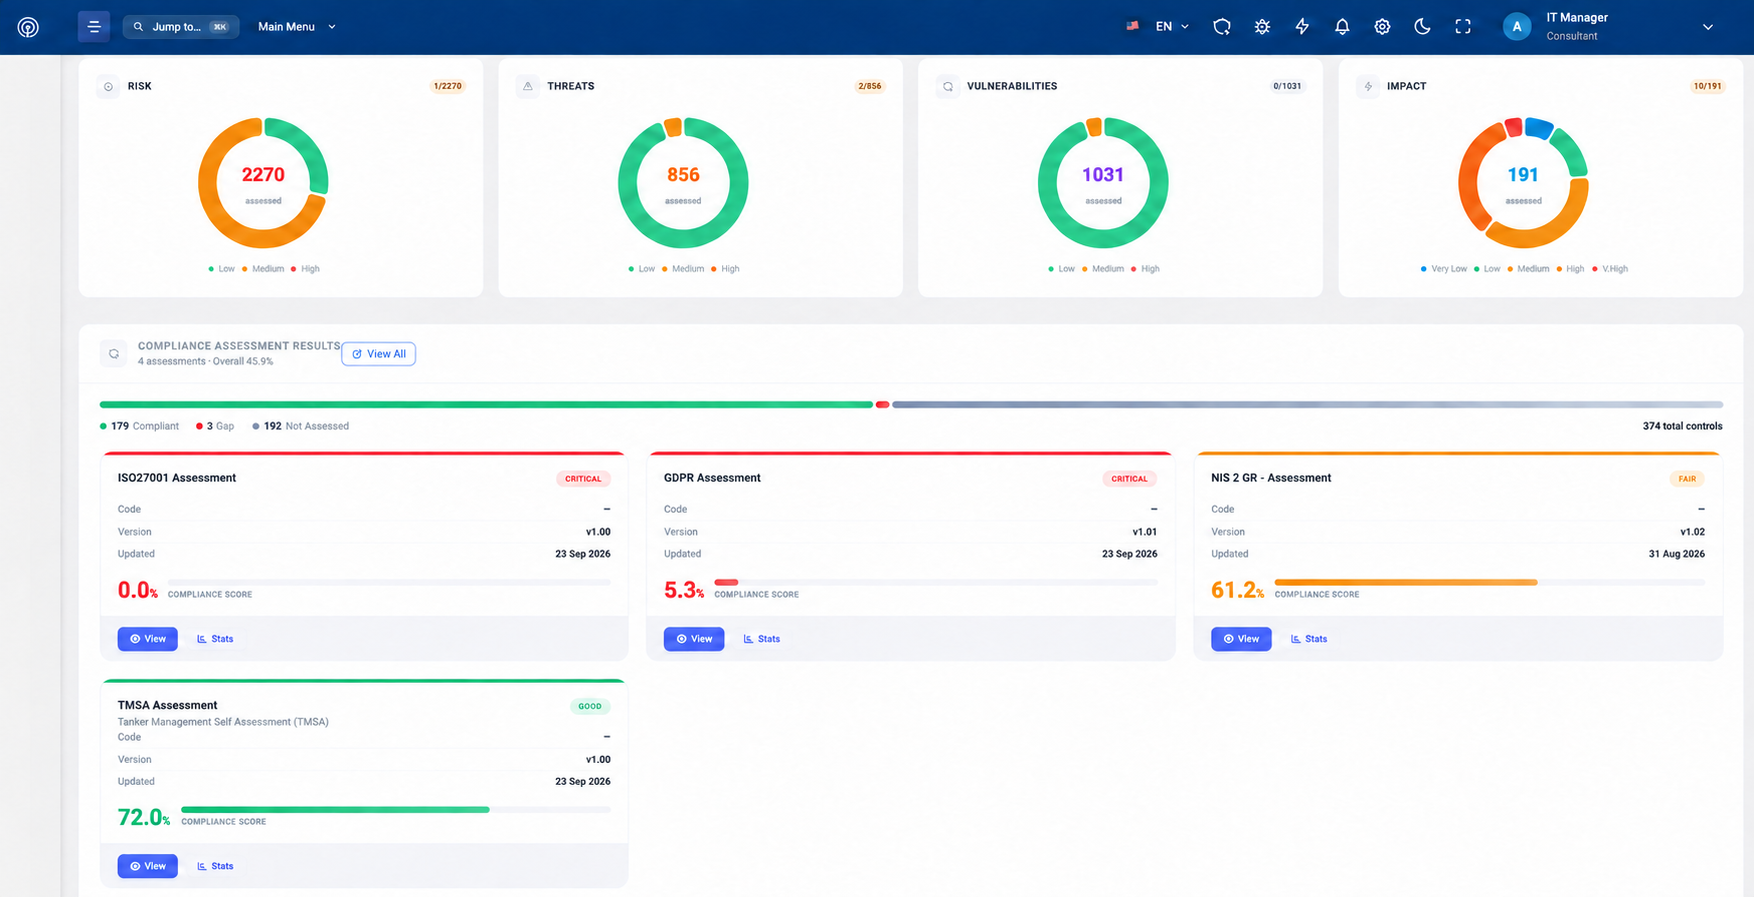
Supported Microsoft Graph checks continuously validate identity, device and security configurations. Results map to ISO/IEC 27001 controls, generate evidence and can pre-populate applicable assessment responses.
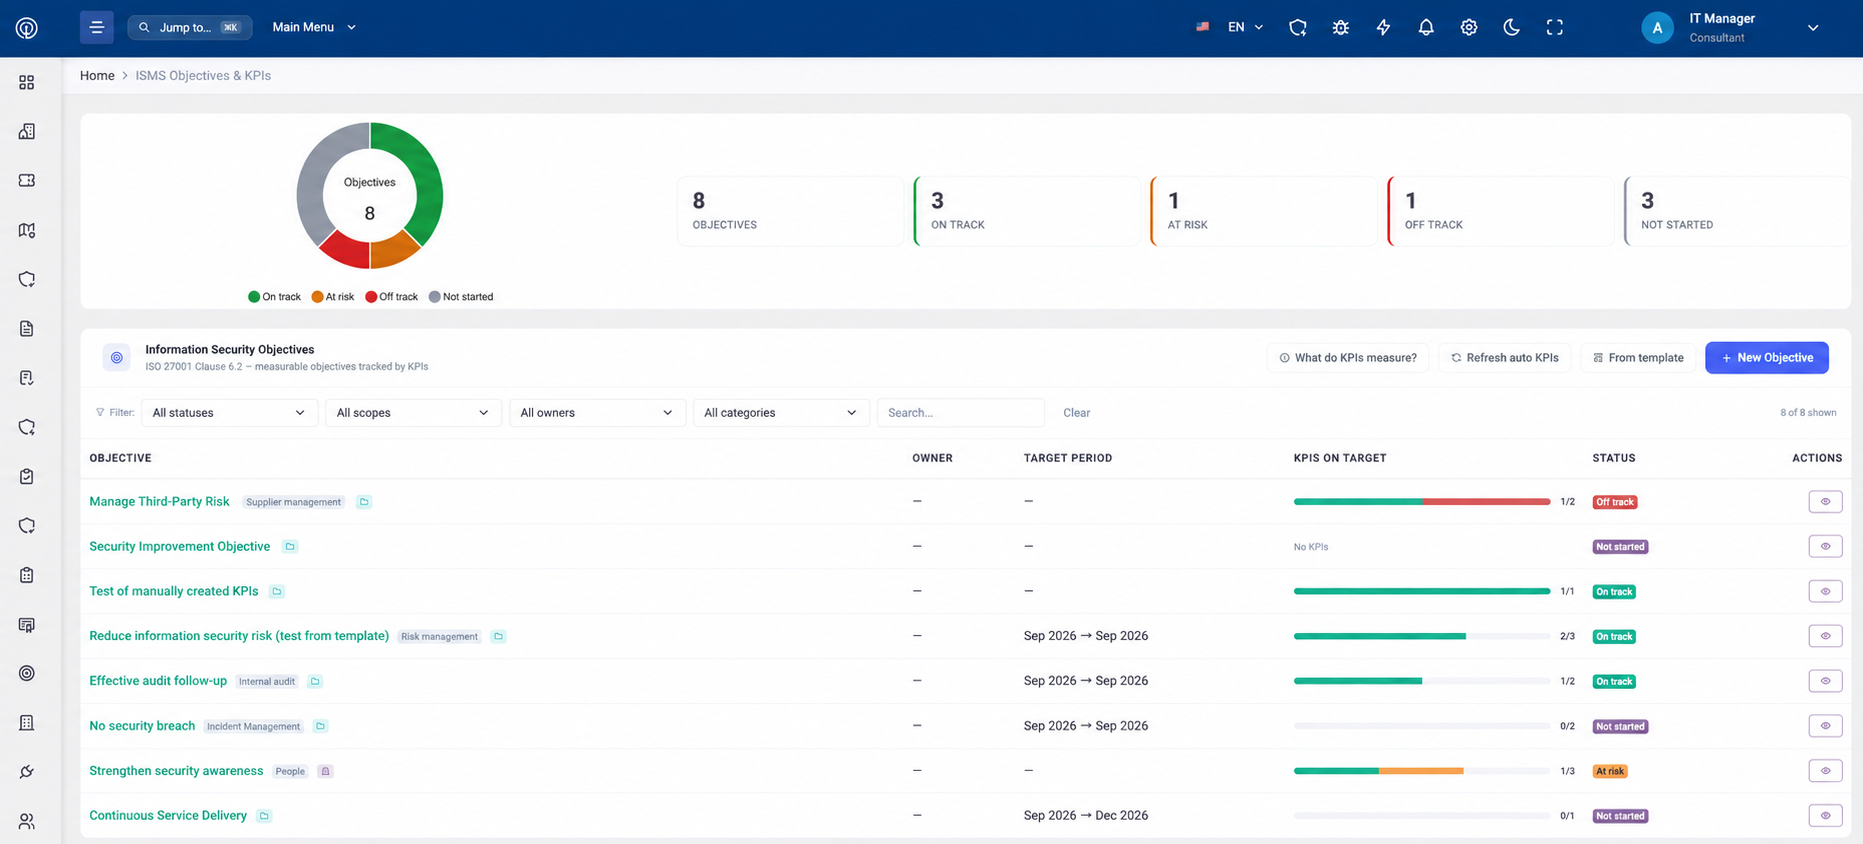
Track measurable information security objectives and use results from risk, compliance, audits, incidents, suppliers and policy acknowledgements as inputs to management review and continual improvement.
The 2022 reference controls are organised into organisational, people, physical and technological themes. Applicability is determined through the organisation's risk-treatment process and recorded in its Statement of Applicability.
Policies, roles, assets, suppliers, incident handling, continuity and wider governance need connected ownership and evidence.
STORM policies · suppliers · incidents · reviewsResponsibilities, awareness and policy acknowledgement depend on clear roles and a reviewable record of participation.
STORM RBAC · owners · acknowledgementsSites, equipment and supporting infrastructure remain part of inventory, dependency, impact and treatment decisions.
STORM cartography · impact · evidenceConfigurations, vulnerabilities, logging, monitoring and remediation can be tied to affected assets, controls and risk decisions.
STORM checks · findings · technical riskCounts and themes follow official ISO/IEC JTC 1/SC 27 material for ISO/IEC 27002:2022. These summaries do not reproduce the licensed Annex A control text.
Use STORM to keep decisions and evidence connected through the full management-system cycle while qualified teams retain responsibility for interpretation and implementation.
Define entities, services, processes, assets, dependencies and interested-party context.
Cartography · contextEvaluate impact, threats and vulnerabilities against defined risk criteria.
Impact · threat · riskSelect controls, document applicability, assign owners and manage actions.
SoA · treatment · policiesMonitor evidence, measure objectives, audit the system and review performance.
Checks · KPIs · auditResolve findings, document decisions and track corrective and improvement actions.
Findings · management reviewA capable platform organises the work. It does not replace organisational judgement or independent assurance.
Use a focused walkthrough to test STORM against your scope, risk method, control set, policy lifecycle, technical evidence, audit programme, objectives and management-review process.