
Elements 1–3G
Governance & people
Leadership and the SMS, shore-based personnel, and the recruitment, management and wellbeing of vessel personnel.
Connect TMSA assessments with policies, risks, fleet context, evidence, findings, objectives and accountable actions—so continuous improvement remains visible between formal review cycles.
The supplied technical description lists TMSA among STORM’s currently supported frameworks. It does not identify the configured edition, complete KPI catalogue, stage logic or a direct SIRE integration; confirm these details for the intended deployment.
For readability, the official elements are summarised below in four editorial groups. These groups do not replace OCIMF’s element structure, KPIs or best-practice guidance.
Leadership and the SMS, shore-based personnel, and the recruitment, management and wellbeing of vessel personnel.
Reliability and critical equipment, navigational safety, plus cargo, ballast, tank cleaning, bunkering, mooring and anchoring.
Change, incidents, safety, environmental and energy management, emergency preparedness and contingency planning.
Measurement, analysis and improvement together with maritime security, including the cyber-security dimension.
The technical description names TMSA as a current framework and documents configurable assessments mapped to STORM’s control library. It does not specify the TMSA edition or an OCIMF/SIRE publishing connection.
STORM’s documented modules create a connected governance layer around the configured TMSA assessment. OCIMF remains the authority for official content, programme access and publication.
Use the supported framework through online assessments, implementation-status tracking, evidence, gaps, reassessment schedules and reports.
Assessment · status · evidenceManage policies and procedures through version control, approvals, acknowledgements, scheduled reviews and an auditable history.
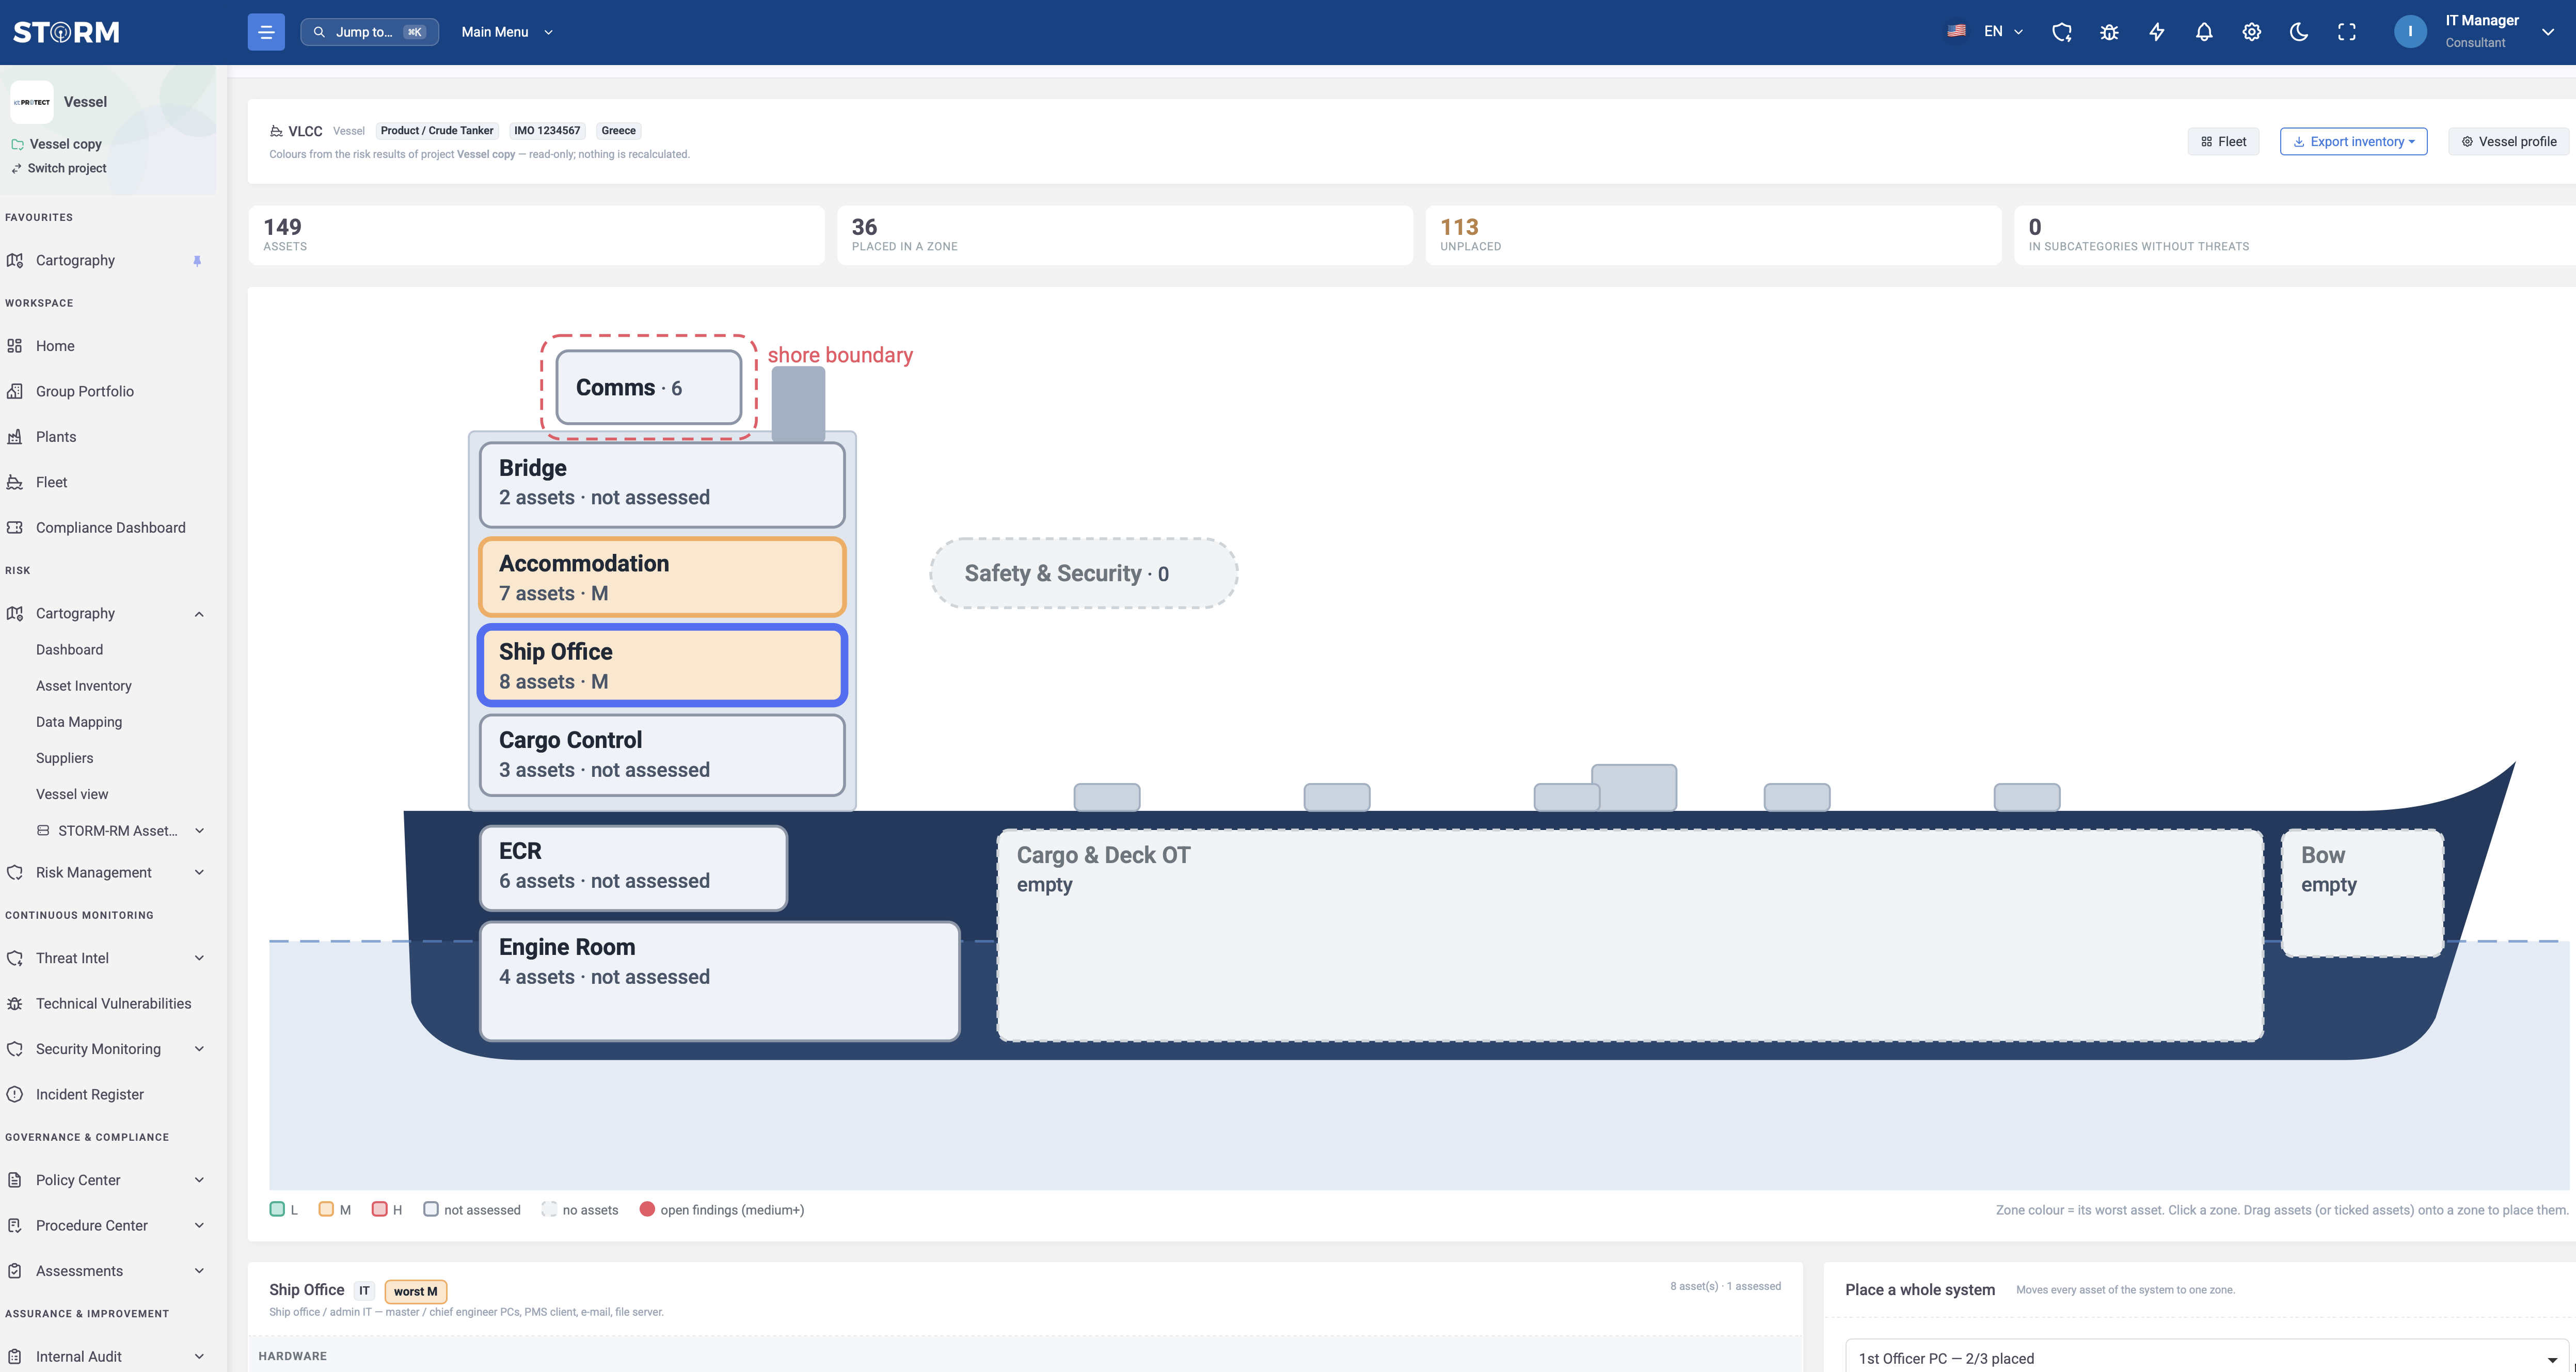
Policy Center · lifecycle · trailConnect services, processes, locations, physical and ICT assets with risks, controls, treatment decisions and action ownership.
Cartography · risk · treatmentPlan internal audits, retain findings, assign remediation owners and monitor progress through a central audit repository.
Findings · owners · remediationRecord security incidents, affected assets, root causes, corrective and preventive actions, target dates and final resolution.
Incident record · root cause · actionTrack defined objectives and KPIs, then consolidate risk, audit, incident, supplier and policy information for management review.
Trends · decisions · improvement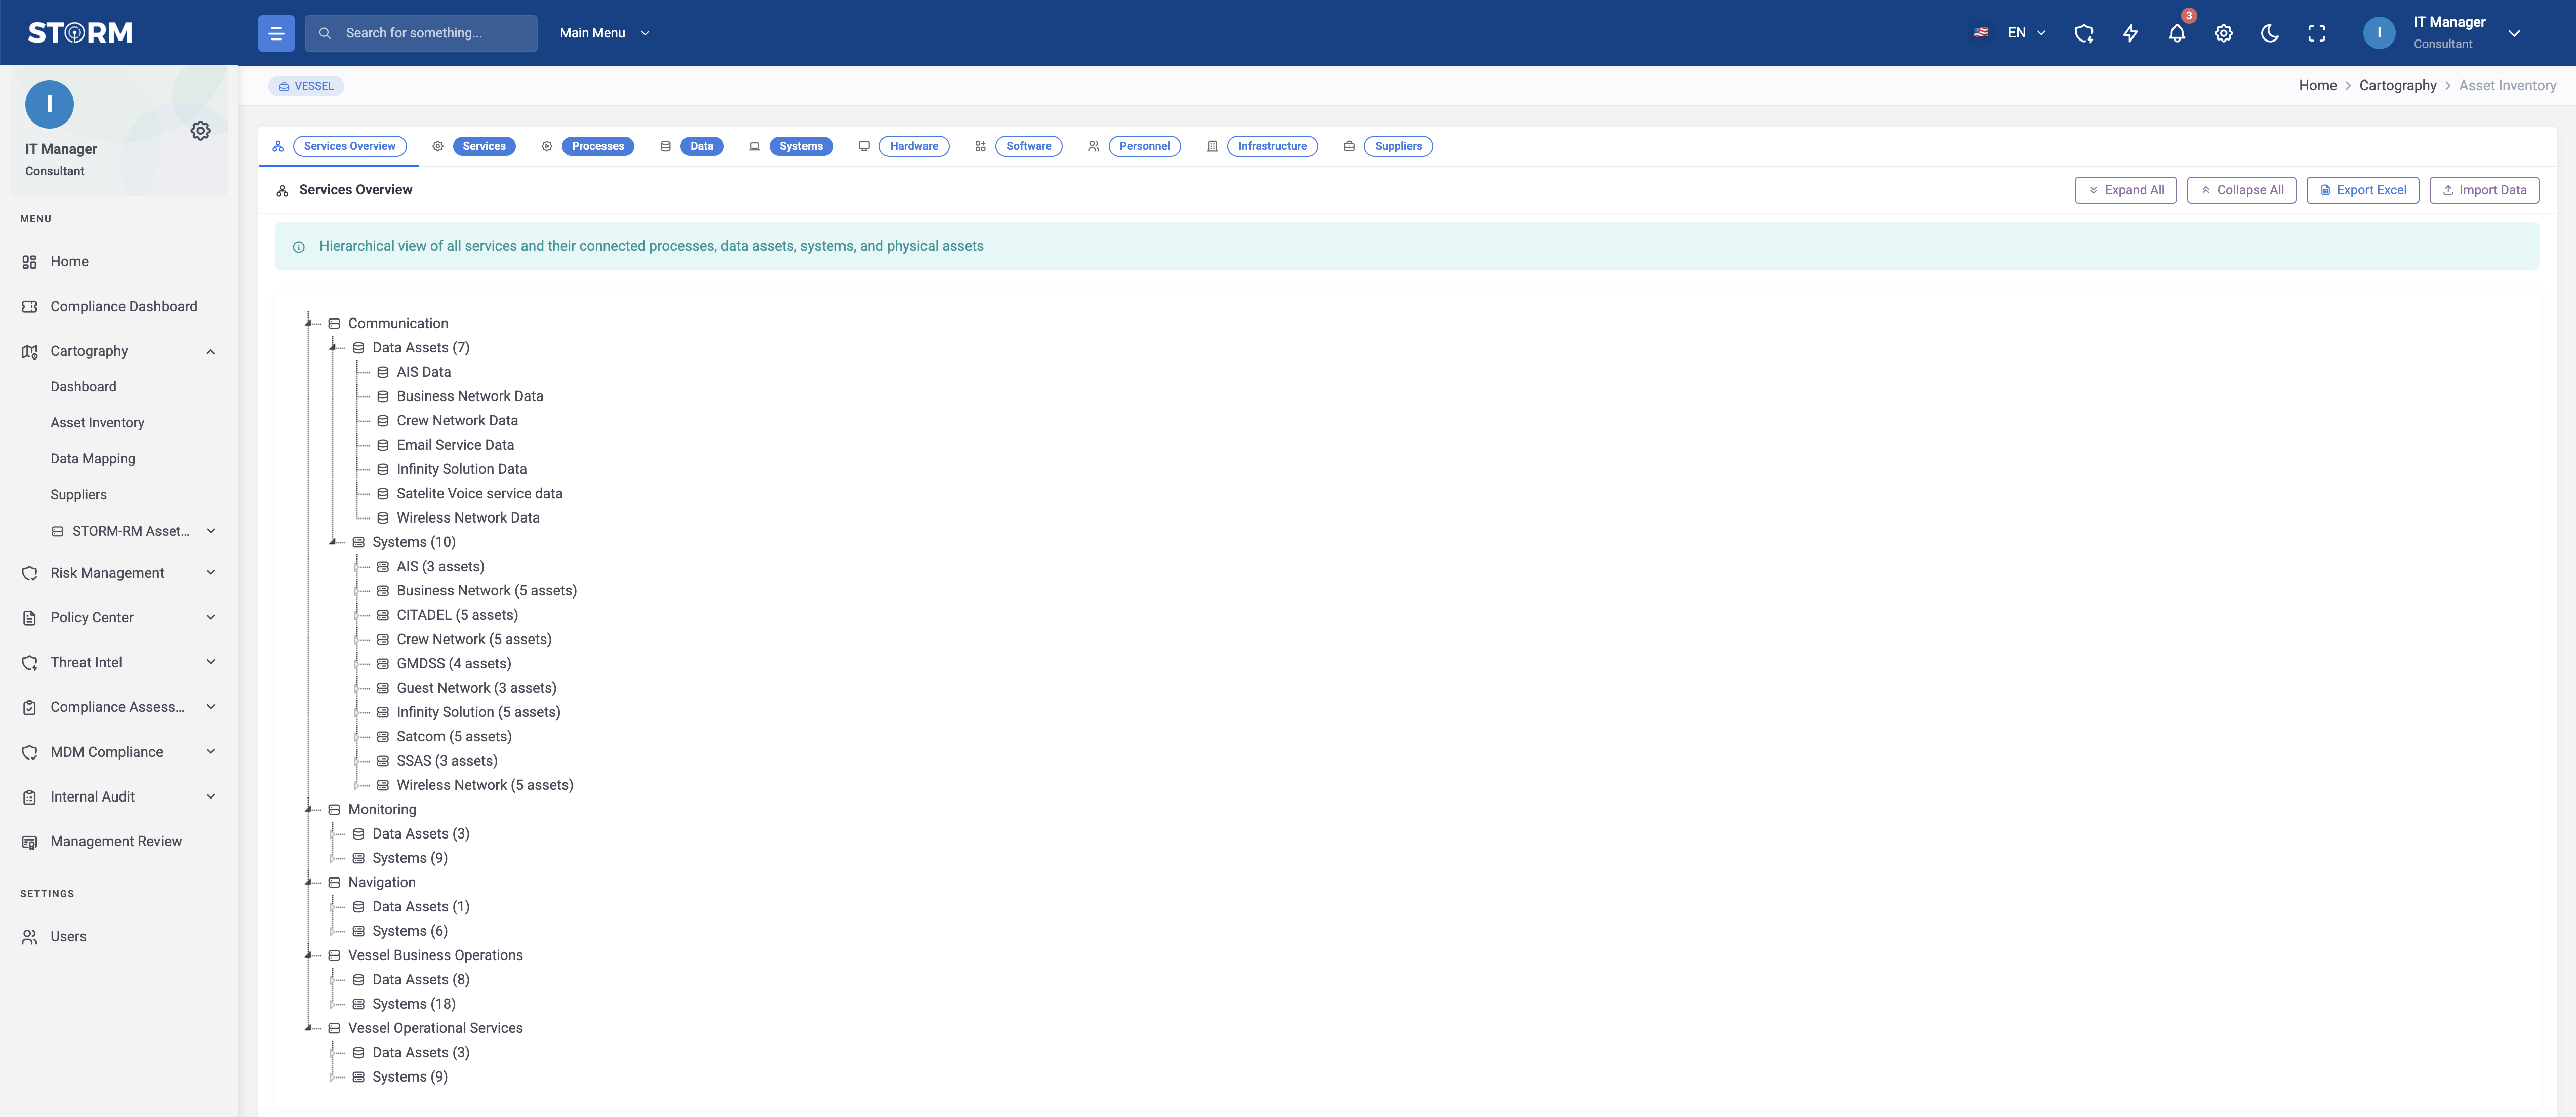
The technical description links supported assessments to status, evidence, gaps and remediation. Policy workflows add version history, approval, acknowledgement and review records behind the management-system answer.
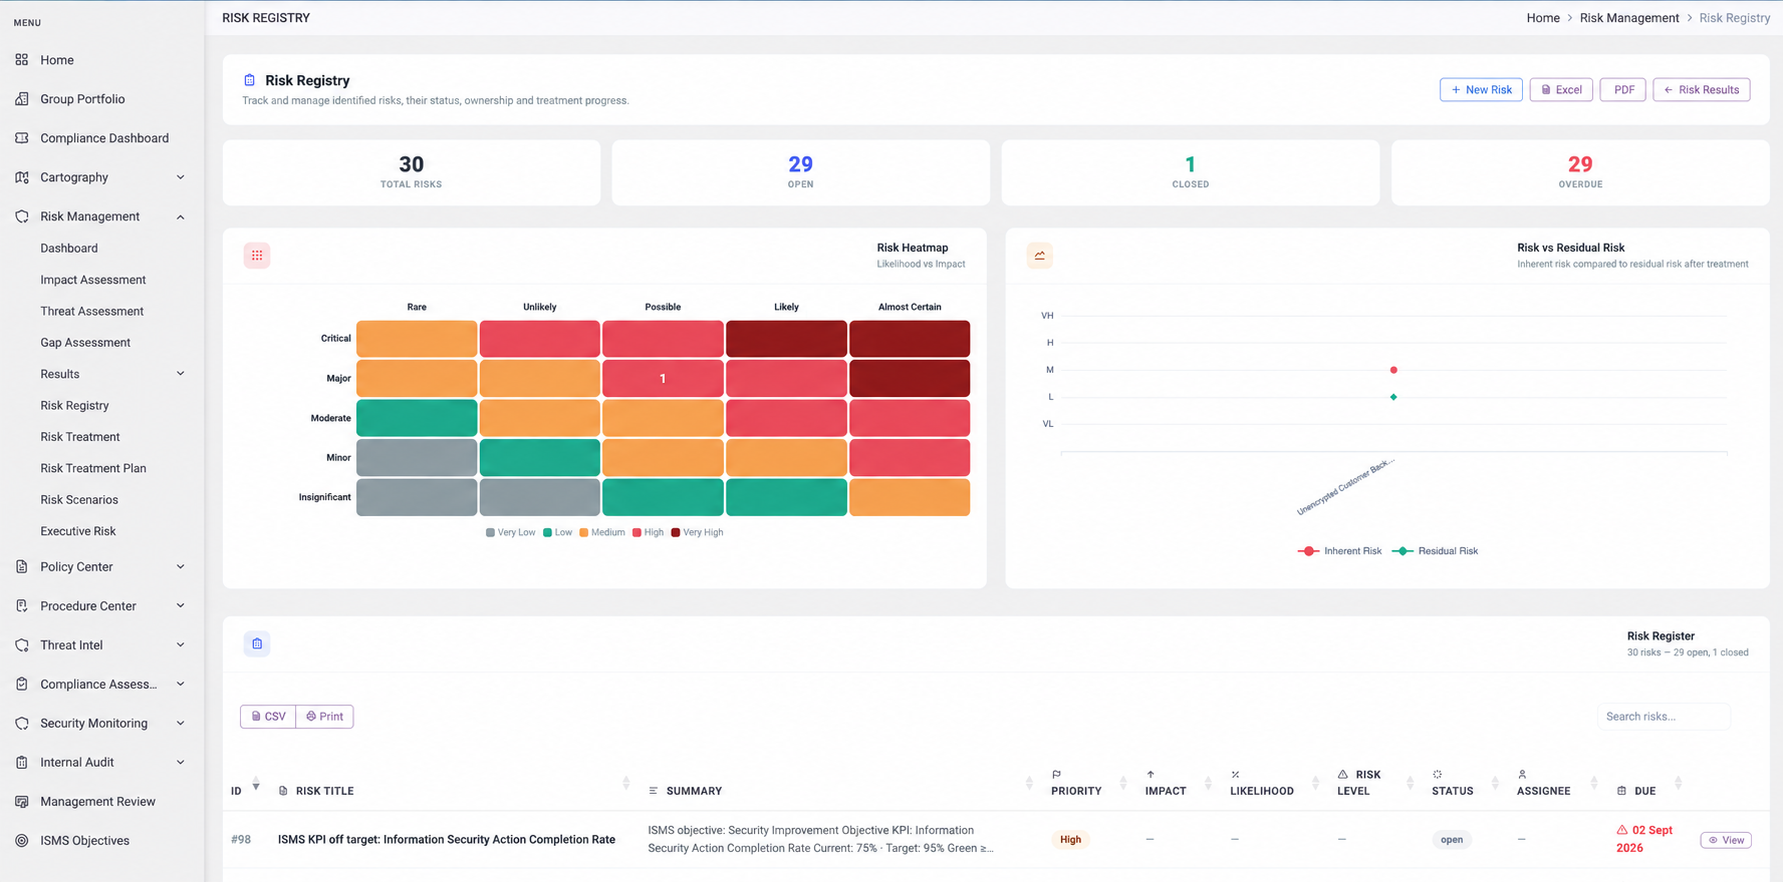
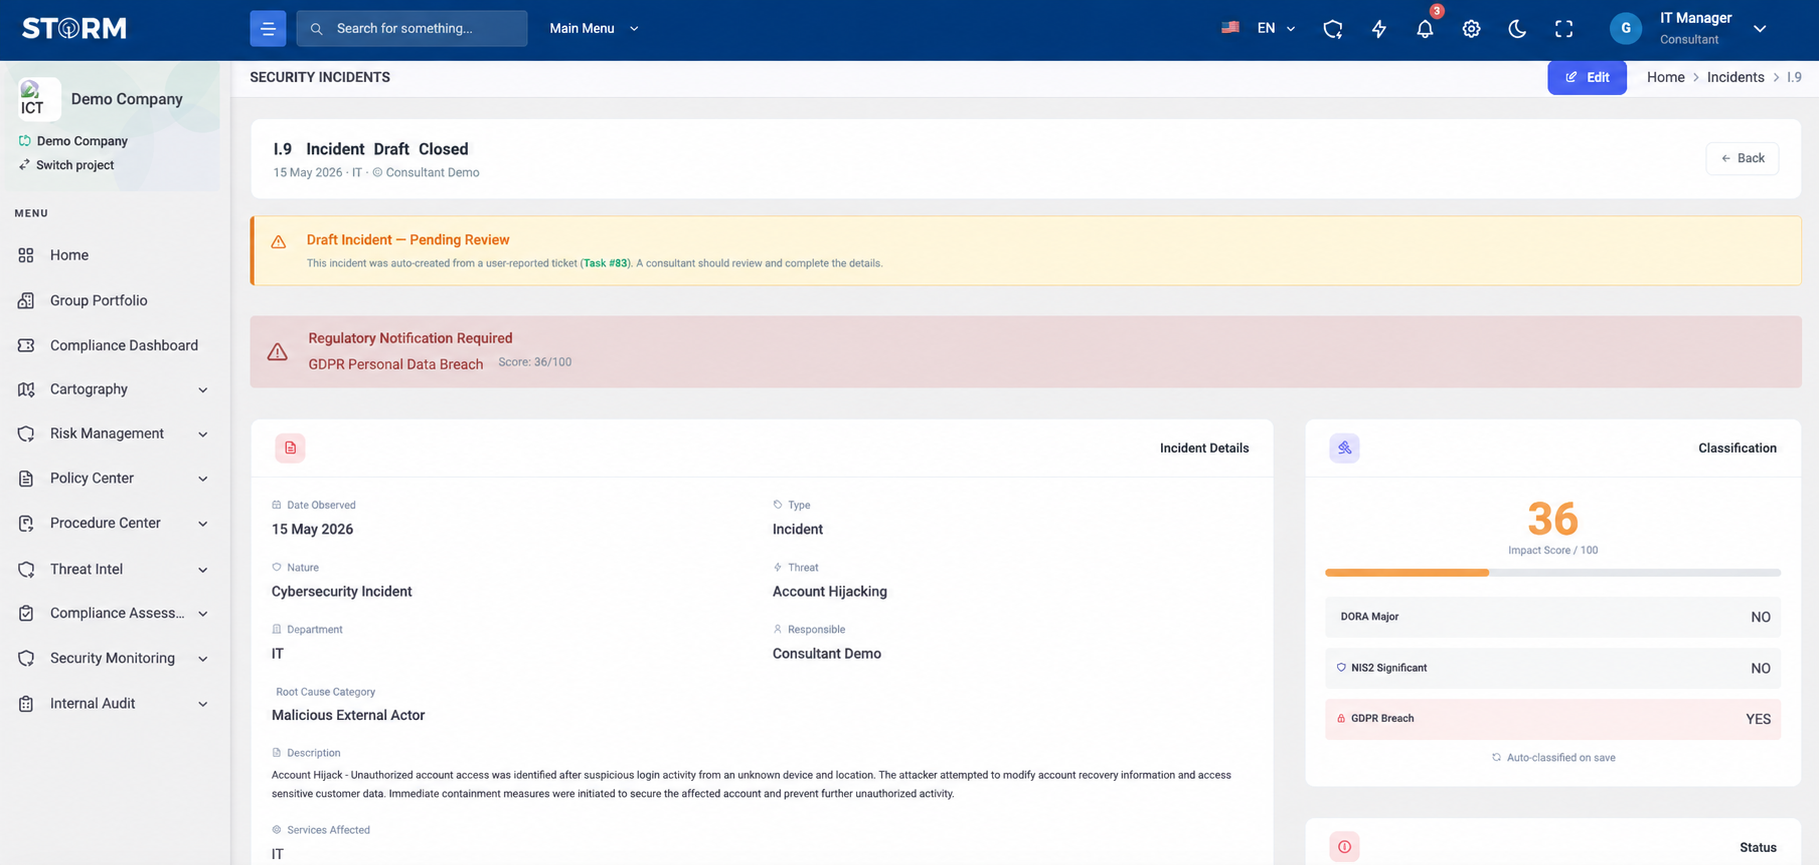
Risks can carry likelihood, impact, controls, treatment, owners, dates and attachments. Security incidents can retain affected assets, root causes and corrective actions. Marine operational incidents remain outside the documented scope unless separately configured.
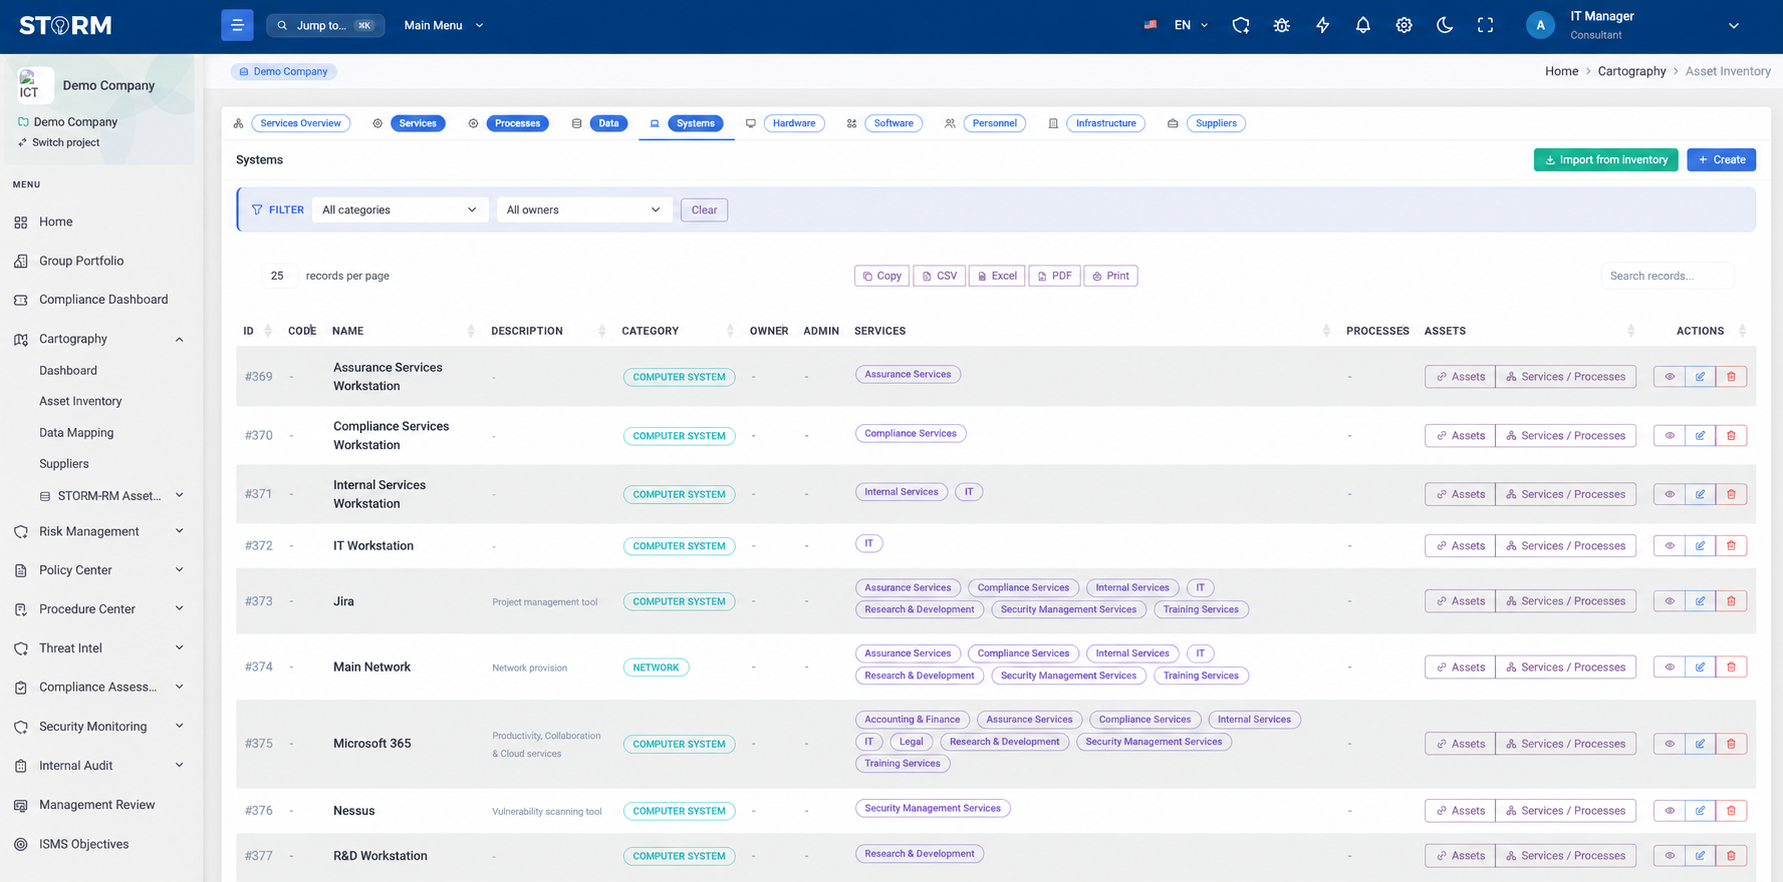
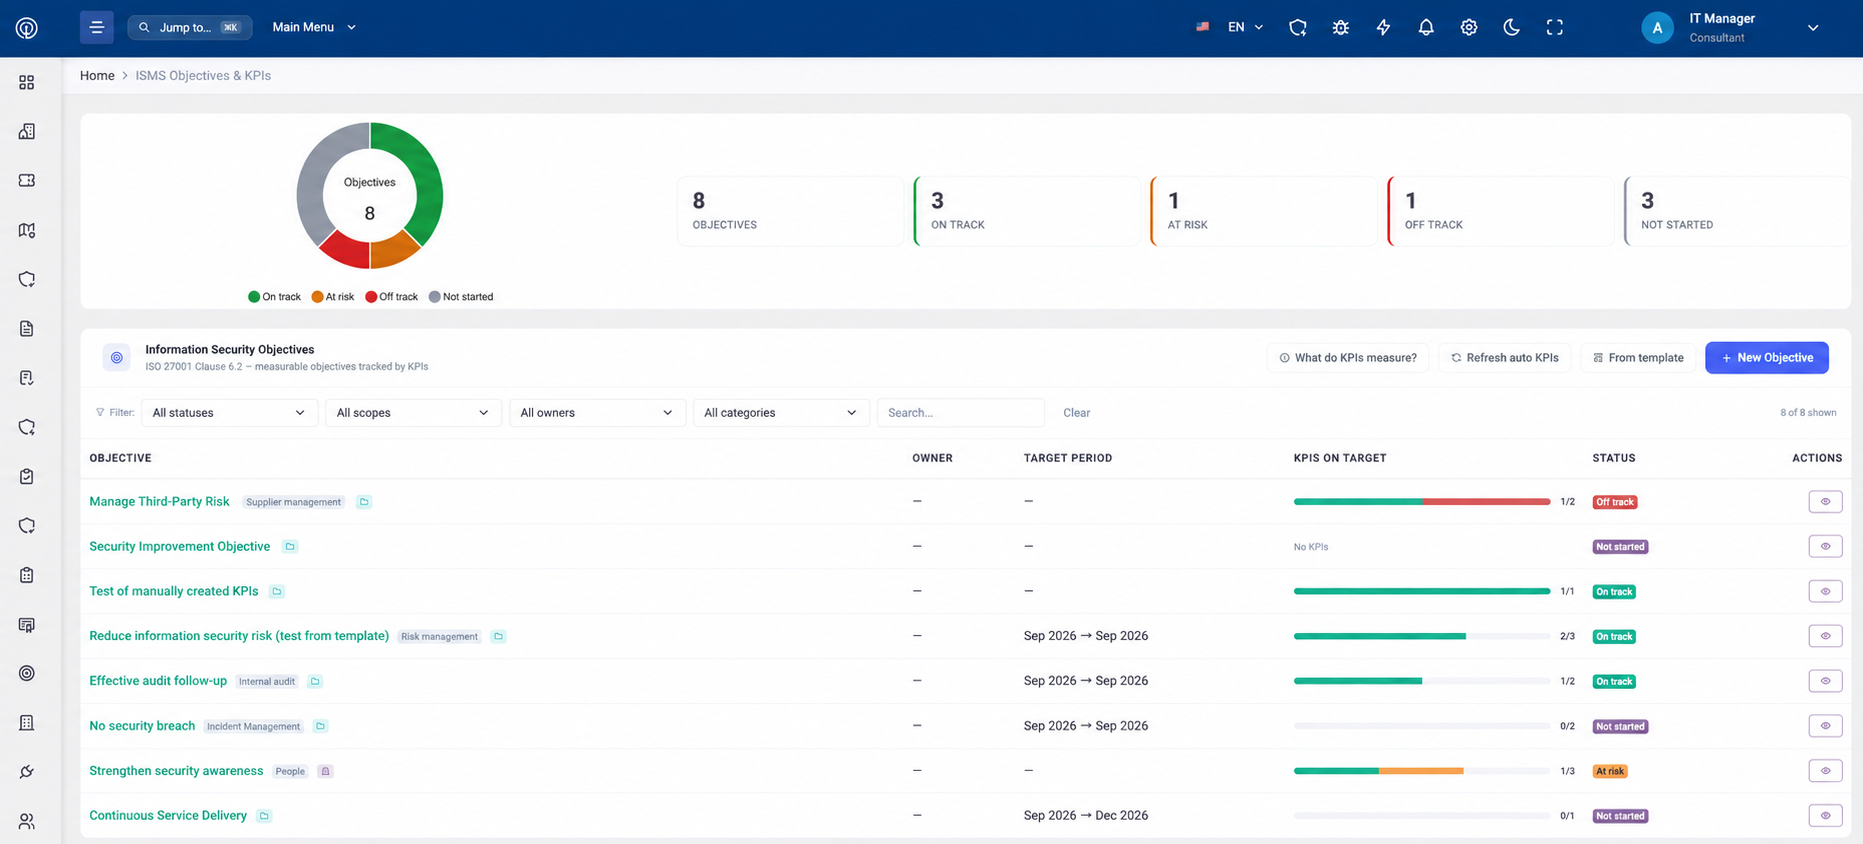
Cartography provides the reusable business and ICT context behind security risks. The objectives and KPI module supports owners, targets, thresholds, monitoring periods and historical trends that can feed management reporting.
OCIMF describes Stage 1 as the minimum expected standard, followed by three stages of increasing standard or performance. Use the official KPIs and best-practice guidance for every conclusion.
The minimum standard expected by the programme and the base from which further improvement is measured.
Minimum expectationThe next set of official KPI expectations, representing a higher management standard than the programme baseline.
Increasing standardA further progression in management performance, assessed only against the applicable official questions and guidance.
Further progressionThe highest of the four stages in the TMSA structure, supported by the corresponding OCIMF best-practice guidance.
Highest programme stageThe page does not reproduce OCIMF’s official KPI catalogue or assign an official TMSA stage.
STORM can organise the supporting programme record. TMSA publication and authorised sharing continue through the applicable OCIMF process.
Verify the applicable OCIMF edition, licensed content, operator access and the TMSA configuration deployed in STORM.
Edition · scope · accessAnswer the official KPIs, retain comments and evidence, and identify the current status by element and stage.
KPI · evidence · statusConvert gaps into risks, findings, document changes, objectives and owned remediation with target dates.
Actions · owners · close-outMonitor improvement, bring results into management review and use SIRE for official creation, editing or publication where applicable.
Review · repeat · publishThat distinction makes the implementation easier to assess and avoids unsupported assumptions about content or publishing.
Walk through the configured edition, elements, KPIs, evidence, policies, risks, findings and actions—and verify how official SIRE publication will be handled.