
Centralize suppliers
Maintain supplier details, categories, relationships and risk status in one repository.
Centralize supplier records, assess business impact and security posture, classify risk, collect supporting evidence and move material findings into accountable remediation.
FortiRecon and BitSight are documented integrations for external supplier-risk signals. Their availability, licensing and configuration should be confirmed for each deployment.
Business impact and security posture combine into a supplier score, tier and documented action path.
A questionnaire alone cannot explain how much a supplier matters or what external exposure changes the decision. STORM connects the supplier record with business impact, compliance responses, vulnerability exposure, disclosed breaches and supporting evidence so risk tiers are tied to visible inputs.
Maintain supplier details, categories, relationships and risk status in one repository.
Apply configurable weighted business-impact criteria and assessment workflows.
Bring together compliance, vulnerability and breach perspectives.
Use risk tiers to guide monitoring, remediation planning or escalation.
The documented workflow combines inventory, configurable assessment, external security context, tiering, reporting and remediation oversight.
Maintain supplier details in a centralized repository, connect records with processes and services through Cartography, and keep categories, locations, contacts, tier status and available external-rating context visible.
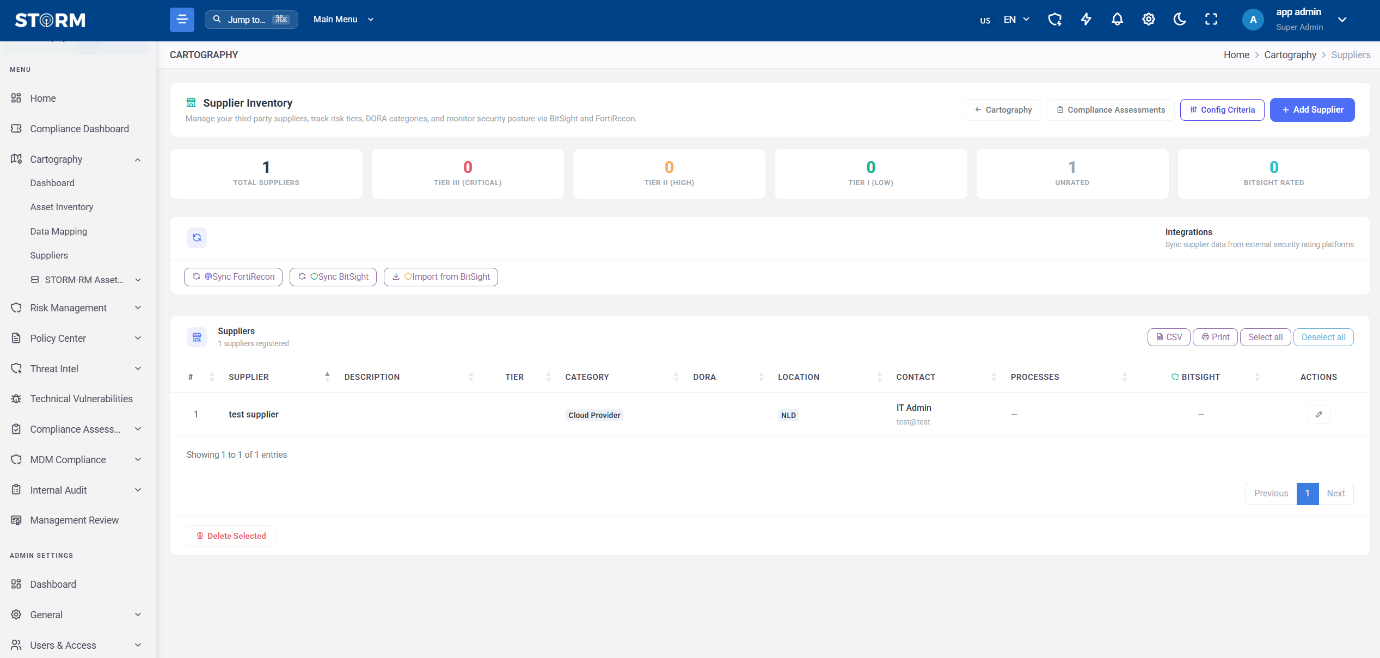
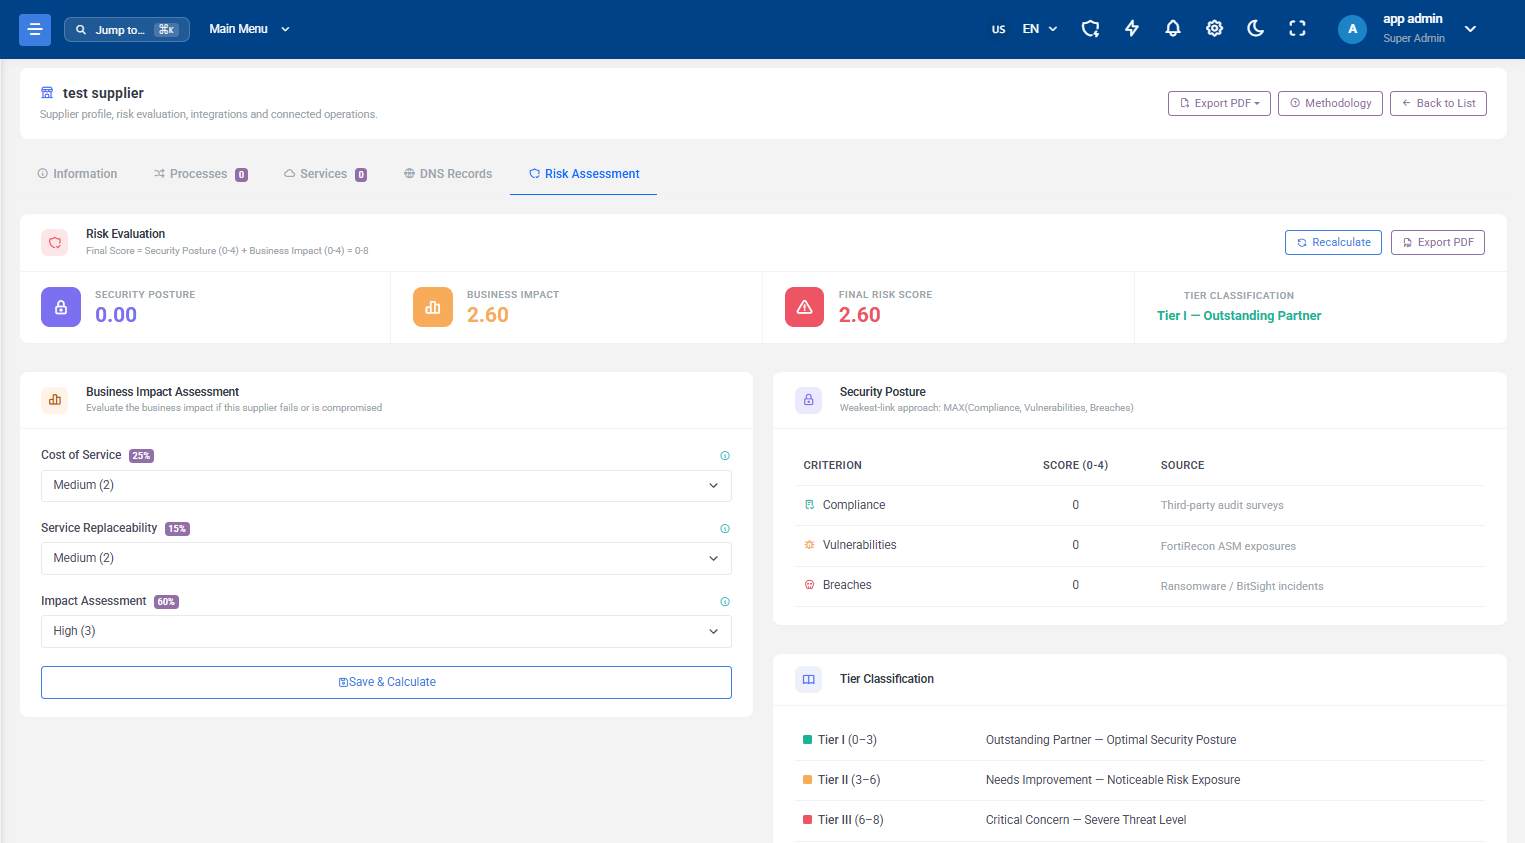
Evaluate each supplier across Business Impact and Security Posture. Business Impact uses configurable weighted criteria, while Security Posture applies a documented weakest-link approach across compliance survey results, vulnerability exposure and security breaches.
Use configurable supplier questionnaires and evaluation workflows. Through the documented Supplier Portal, suppliers can respond against selected frameworks, report implementation status and upload supporting evidence for individual controls.
Use documented FortiRecon and BitSight integrations to retrieve external threat, breach or security-rating context for third-party monitoring and scoring. These signals inform the assessment; they do not replace the business-impact or compliance view.
Use the combined score to classify suppliers into three documented tiers and guide continuous monitoring, remediation planning or immediate action. Supplier risks can also be managed in the Risk Registry with owners, controls, treatment details, review dates and attachments.
STORM preserves the inputs behind each tier so teams can see why a supplier was prioritized and what follow-up the result requires.
Supplier and relationship context
Business impact criteria
Questionnaire and evidence
External security signals
Final score and risk tier
Monitor or remediate
Validate methodology settings, questionnaire content, integration prerequisites and remediation governance against the third-party programme you intend to run.
Bring one supplier, its service relationship, a completed questionnaire, representative external signals and an open remediation action to the walkthrough.
Validate the supplier record, business-impact criteria, questionnaire evidence, external security context, tier result and remediation path against your operating model.