
STORM GRCOperational advantage
Twelve connected modules sharing the same asset, control and risk model.
Risk & complianceAudit & incidentsSuppliers & BCPPolicies & threat intel
STORM connects compliance to the operational work around it: assets, risk, audits, incidents, suppliers, continuity, policies, tasks and threat intelligence. Vanta describes an automated trust platform spanning compliance, risk and customer proof. Compare the published approaches and see where STORM provides the broader operational model.
Source-backed comparison · Vanta information links to Vanta's official website · Reviewed 30 September 2026
Twelve connected modules sharing the same asset, control and risk model.
Automation-led compliance, risk, audit, third-party risk and customer trust workflows.
STORM is designed for teams that want framework work, operational risk and security governance to run on the same underlying model—not in separate trackers.
Assets, controls and risks are shared across compliance, audit, supplier and incident workflows, reducing re-entry between modules.
Platform architectureCartography, business impact, threat and vulnerability assessment feed the risk register, treatment plans and compliance monitoring.
Five-phase methodologyPublished STORM coverage includes NIS 2, DORA, NERC CIP, VDA ISA and IMO MSC.428(98), alongside ISO, NIST, SOC 2 and GDPR.
Regulated sectorsSTORM publishes EU-hosted SaaS under EU jurisdiction and offers on-premise deployment discussions for strict data-locality requirements.
Data locationThis focused comparison avoids raw feature counts and highlights areas where STORM's published scope is more operationally explicit—from asset cartography and continuity to incidents, policies and sector workflows.
This is a focused view of STORM's published differentiators, not a complete feature inventory. It does not imply that an unlisted Vanta capability is unavailable; validate requirements in current demonstrations and contracts.
The value proposition is the path between modules: one set of assets, risks and controls moving through assessment, treatment, evidence and governance.
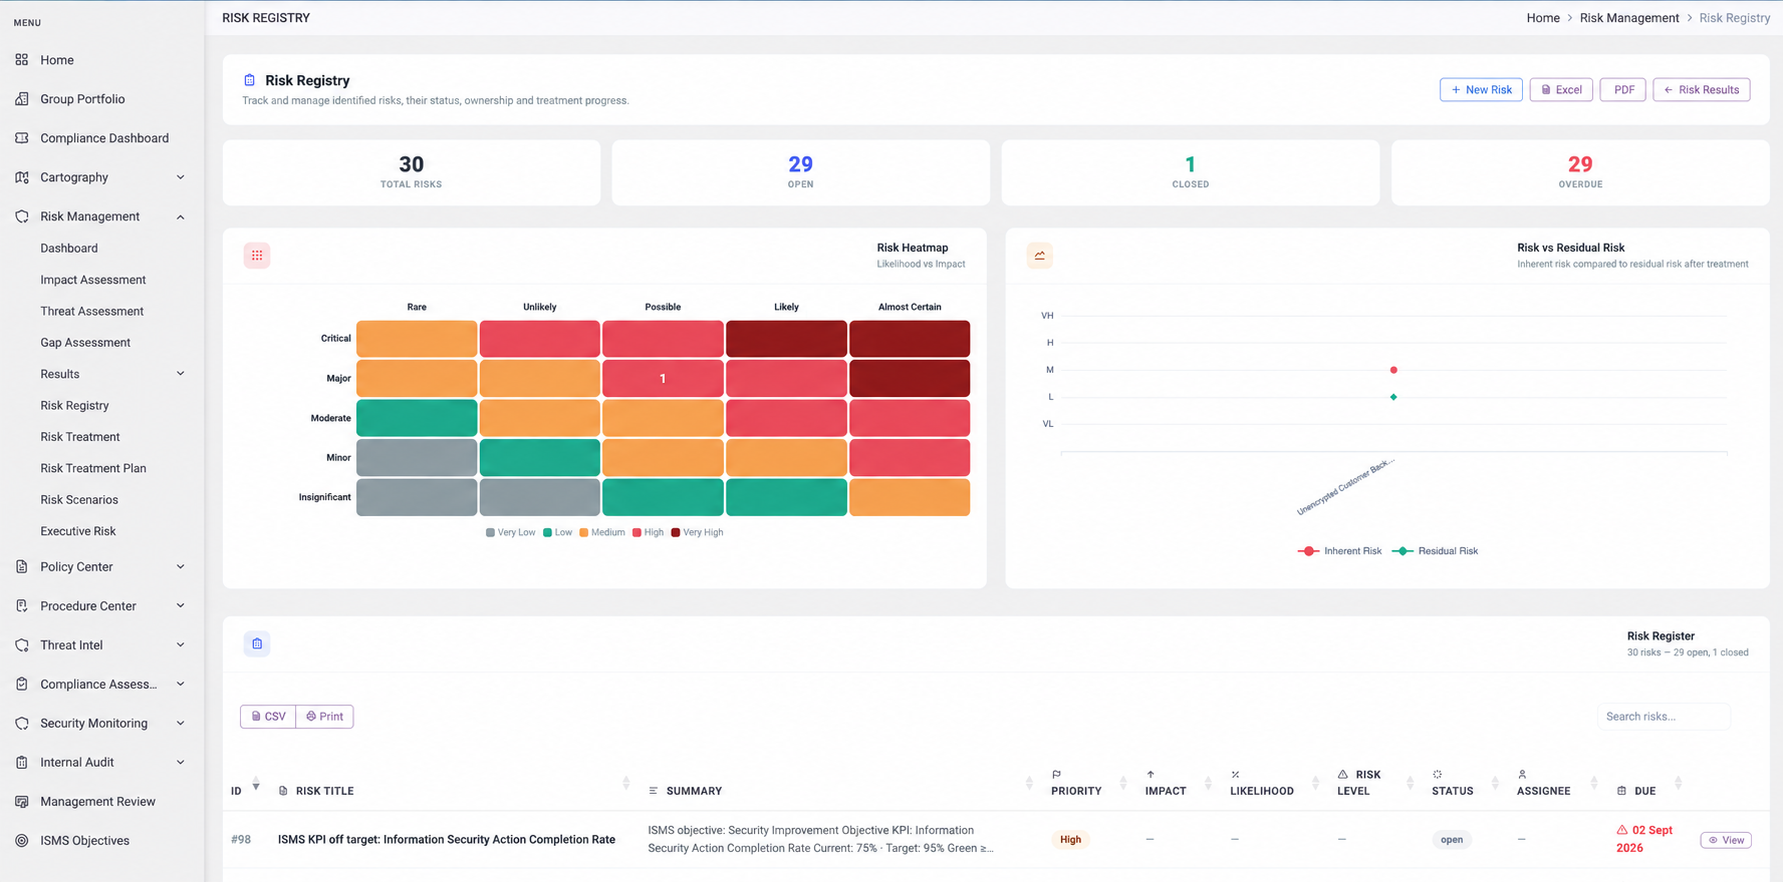
STORM ties impact and threat assessment to risk scenarios, treatments and residual risk, so framework activity stays connected to the underlying exposure.
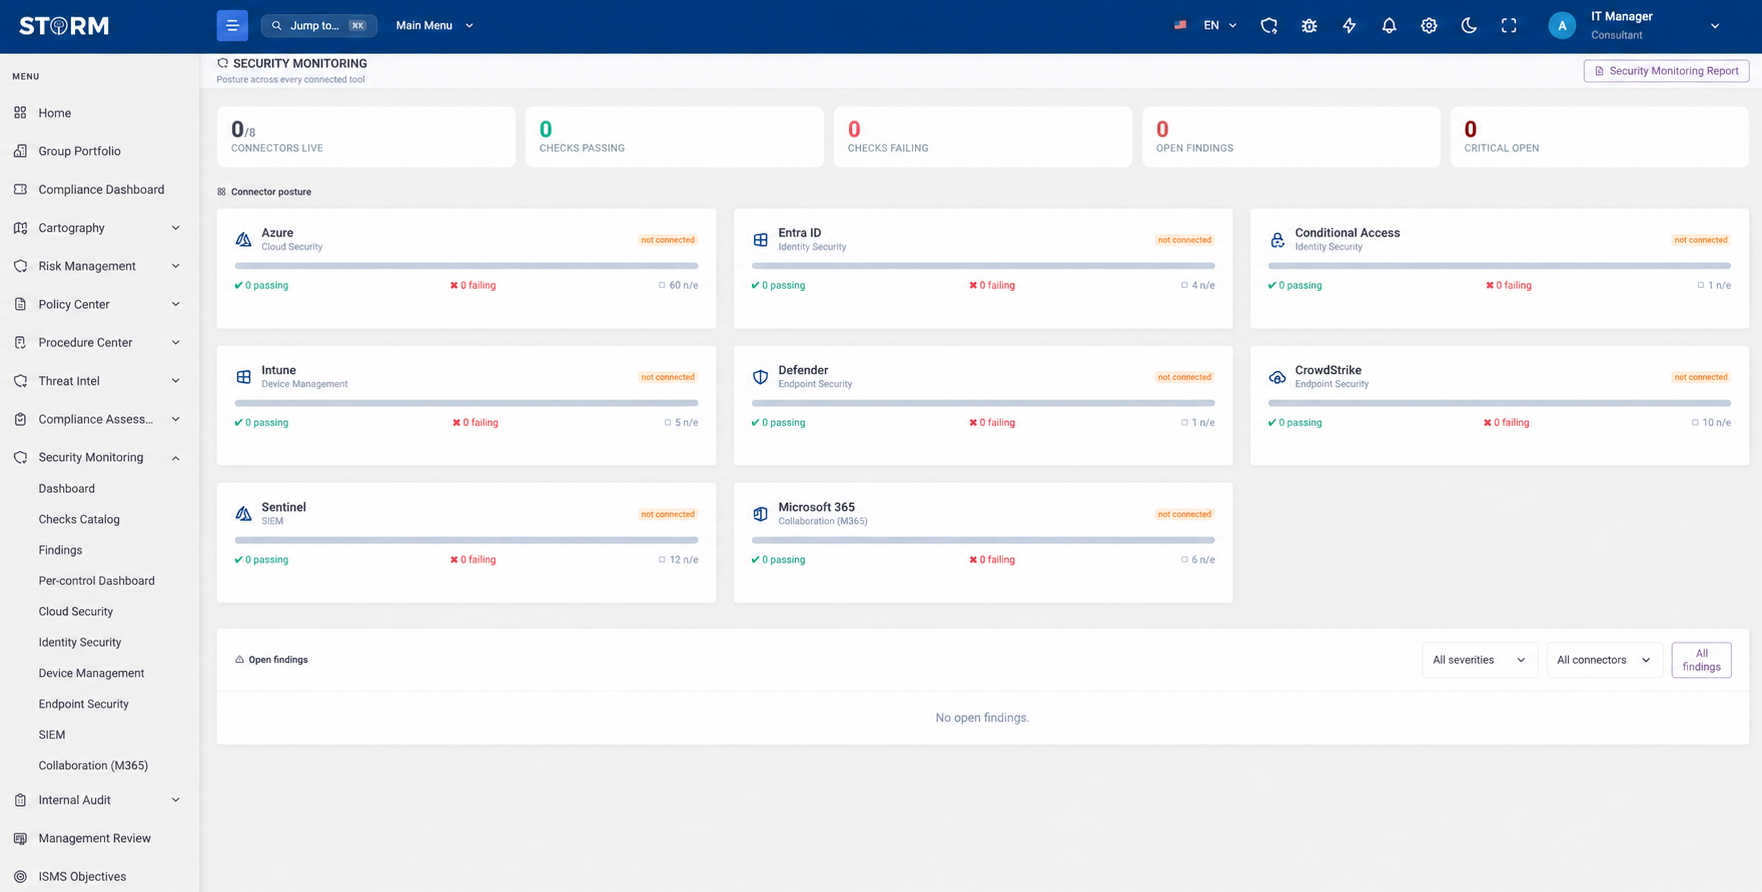
Supported MDM and EDR integrations can pre-populate endpoint posture, configuration state and asset attributes. Remediation tasks and audit findings can then sync to Jira or Teams.
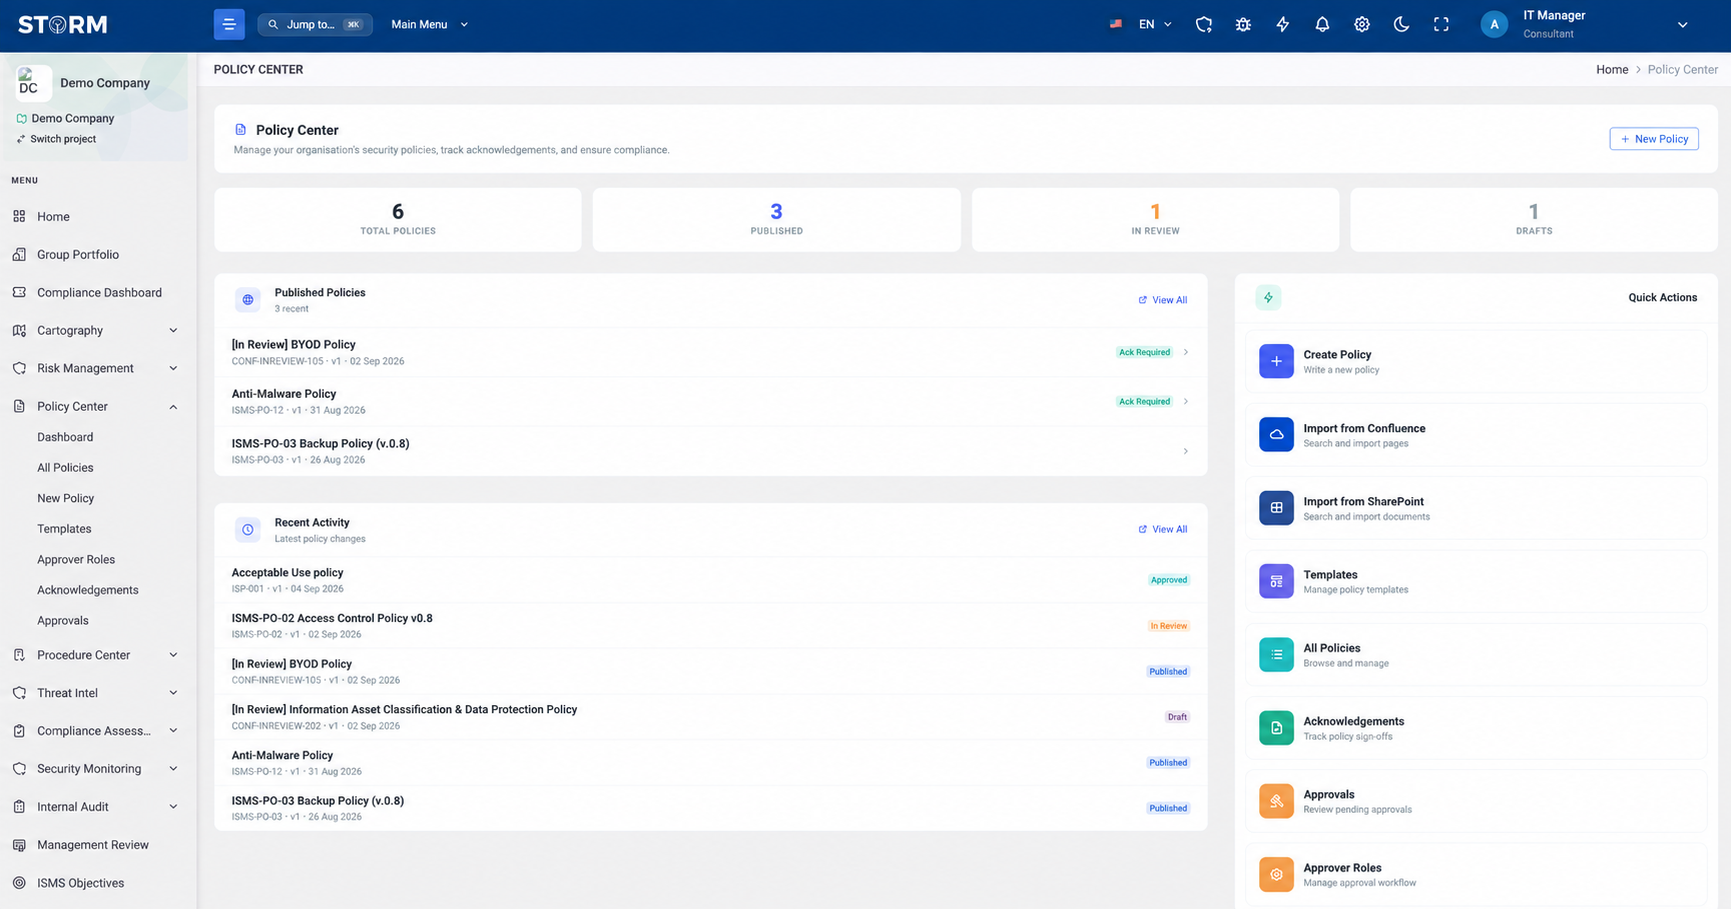
Policies move through draft, review, approval and archive states, retain version history and map directly to framework controls.
Bring your actual frameworks, evidence sources, reporting needs and deployment constraints to the STORM demonstration.
Use a 30-minute session to test STORM against your assets, controls, evidence sources, reporting needs and deployment constraints.